¡Oferta!

CWP7 Tweak Manager

El precio original era: 99,00 €.El precio actual es: 67,00 €.

CWP7 Tweak Manager is an all-in-one CWP7 server maintenance and diagnostics toolkit for AlmaLinux. Fix account ownership and permissions, manage IPv6, CSF, quotas, SSL, FTP TLS, SpamAssassin, IP reputation monitoring and more through a clear, state-aware GUI with safe checks, confirmations and post-action verification.

Descripción

⚙ CWP7 Tweak Manager

A powerful all-in-one maintenance, diagnostics, security, mail,
networking and servidor repair toolkit created specifically for
CWP7 / Control Web Panel administrators.

CWP7 Admin Module
AlmaLinux Ready
GUI Servidor Tweaks
Smart Diagnostics
Licensed Product

Take Control of Your CWP7 Servidor Without Constantly Returning to SSH

If you manage CWP7 servers, you already know that many of the most
important troubleshooting, maintenance and optimization tasks still
require SSH access.

A website suddenly returns a 403 error. Files have been extracted as
root:root. SpamAssassin appears to be running but spam
continues reaching your mailbox. CSF is pointing to unexpected iptables
paths. IPv6 needs to be disabled. XFS quotas need to be configured.
A CWP hostname certificate is correct on disk but the panel is still
serving an older certificate.

The normal solution is to search through your notes, connect through SSH,
locate the correct configuration file, make a backup, run several commands,
restart a service and then hope everything worked correctly.

CWP7 Tweak Manager changes that workflow.
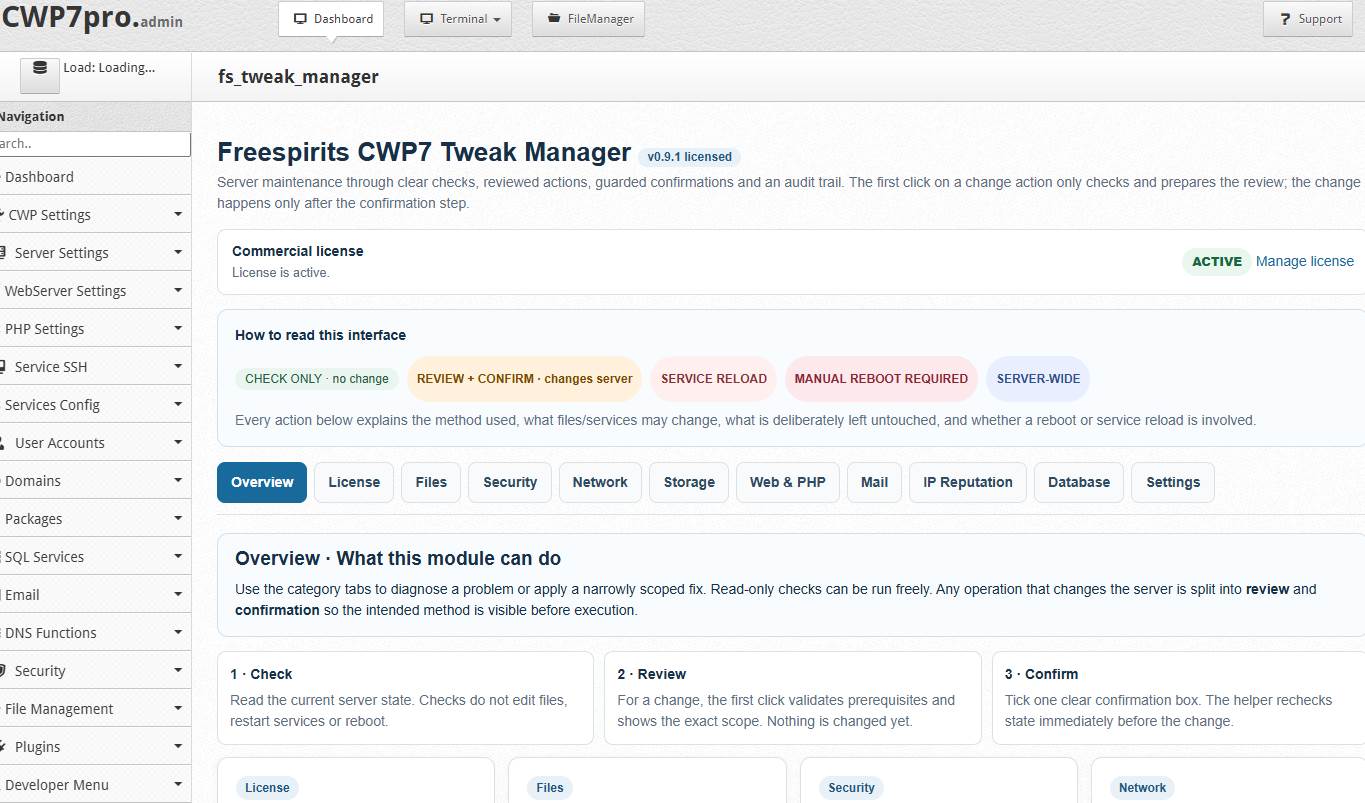
It brings frequently used CWP7 administration procedures into one
organized graphical interface with diagnostics, explanations,
confirmation steps and post-operation verification.

This is not a collection of blind one-click optimization scripts.
CWP7 Tweak Manager is designed around a much safer philosophy:

Check → Understand → Review → Confirm → Apply → Verify

A Central Maintenance Console for CWP7

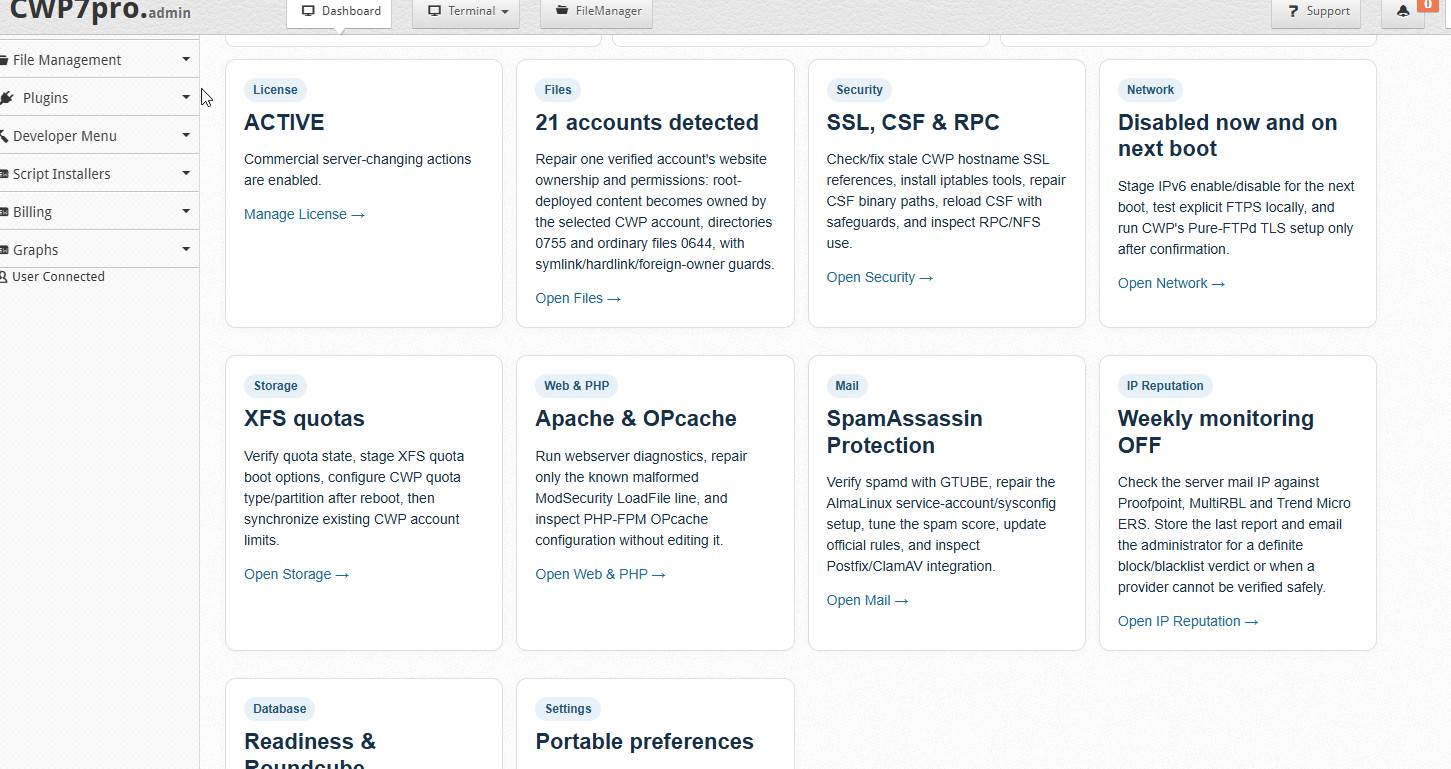
CWP7 Tweak Manager organizes servidor administration into clear sections,
so you can quickly find the type of operation you need.

📁 Files

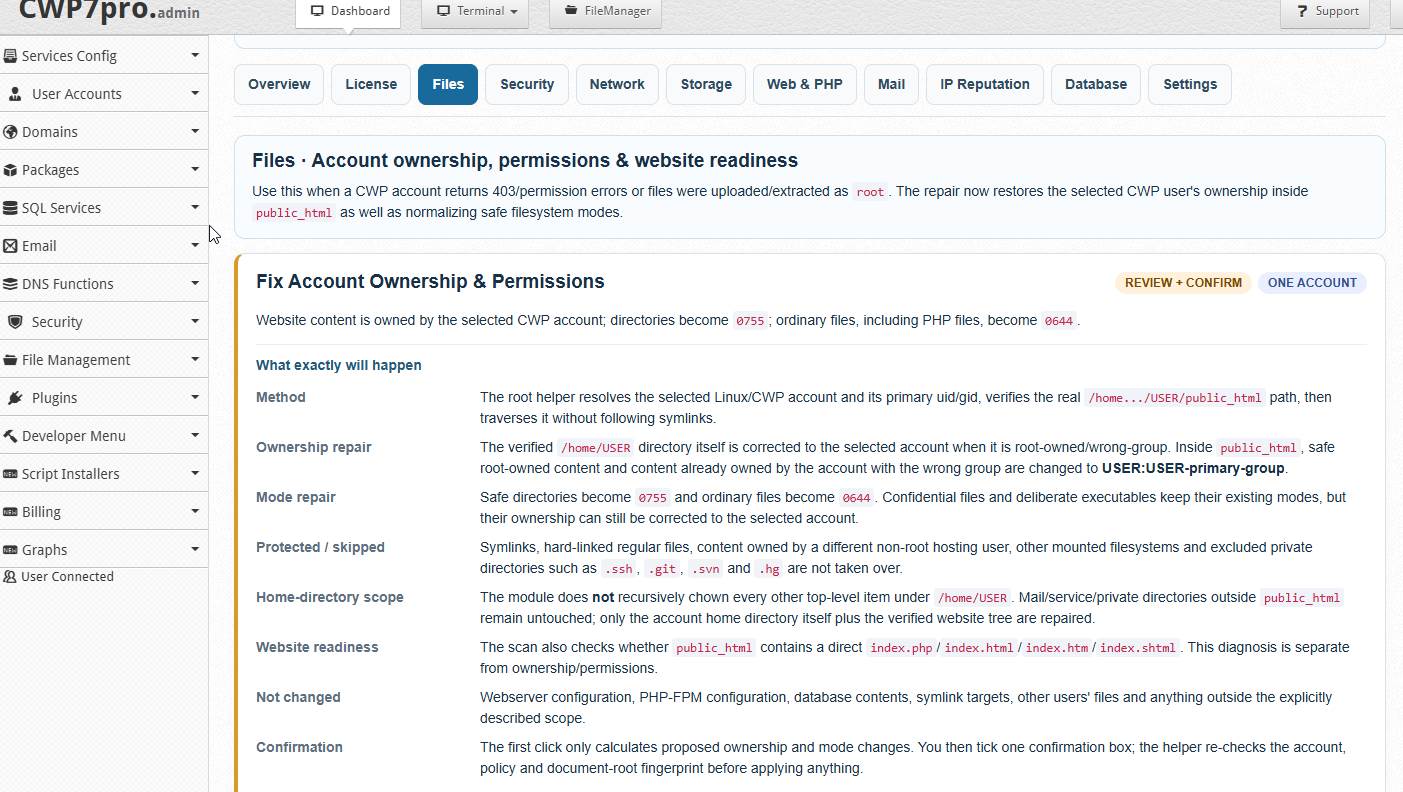
Account ownership repair, permissions normalization and document-root diagnostics.

🛡 Security

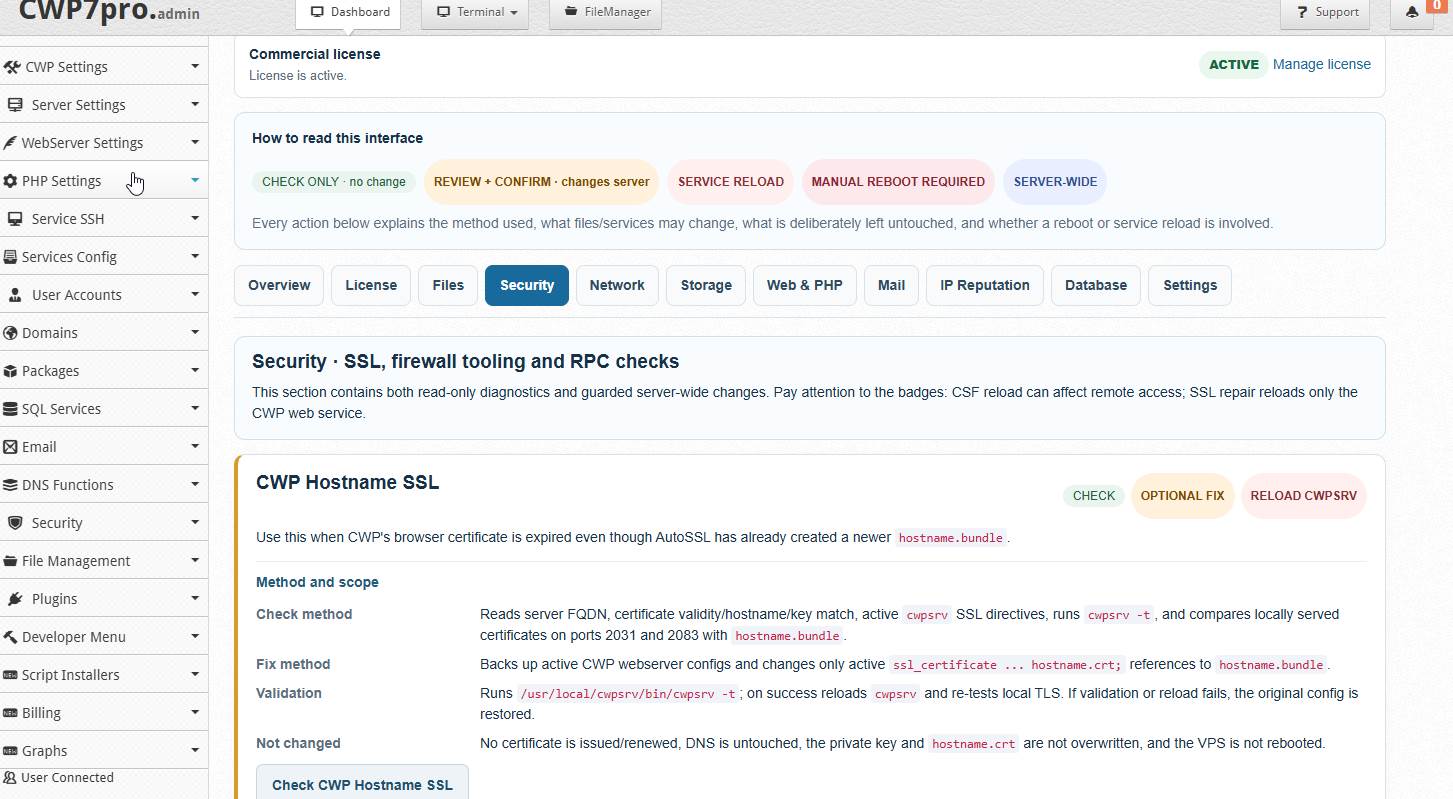
CWP SSL diagnostics, CSF tooling, iptables validation and RPC checks.

🌐 Network

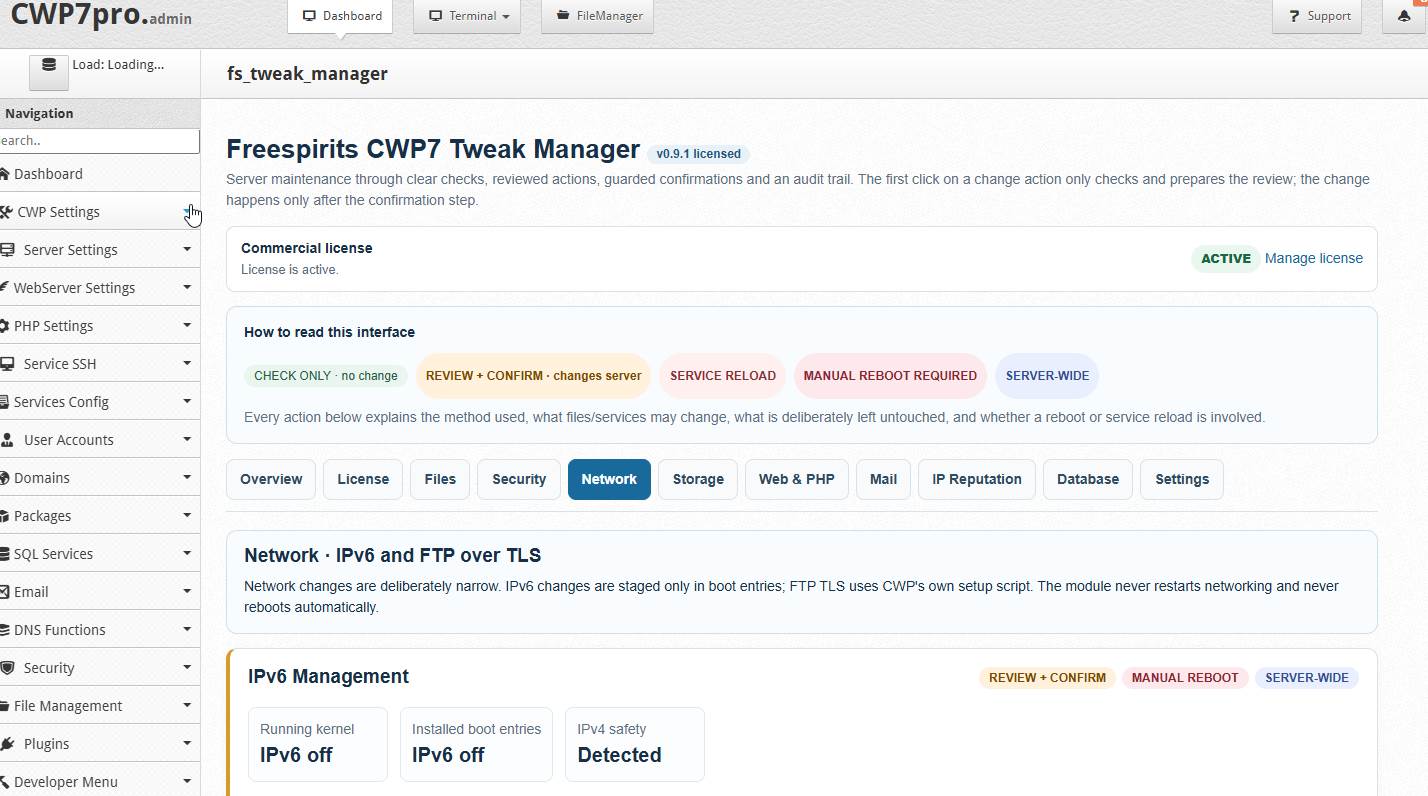
IPv6 management, FTP TLS diagnostics and networking-related tweaks.

💾 Storage

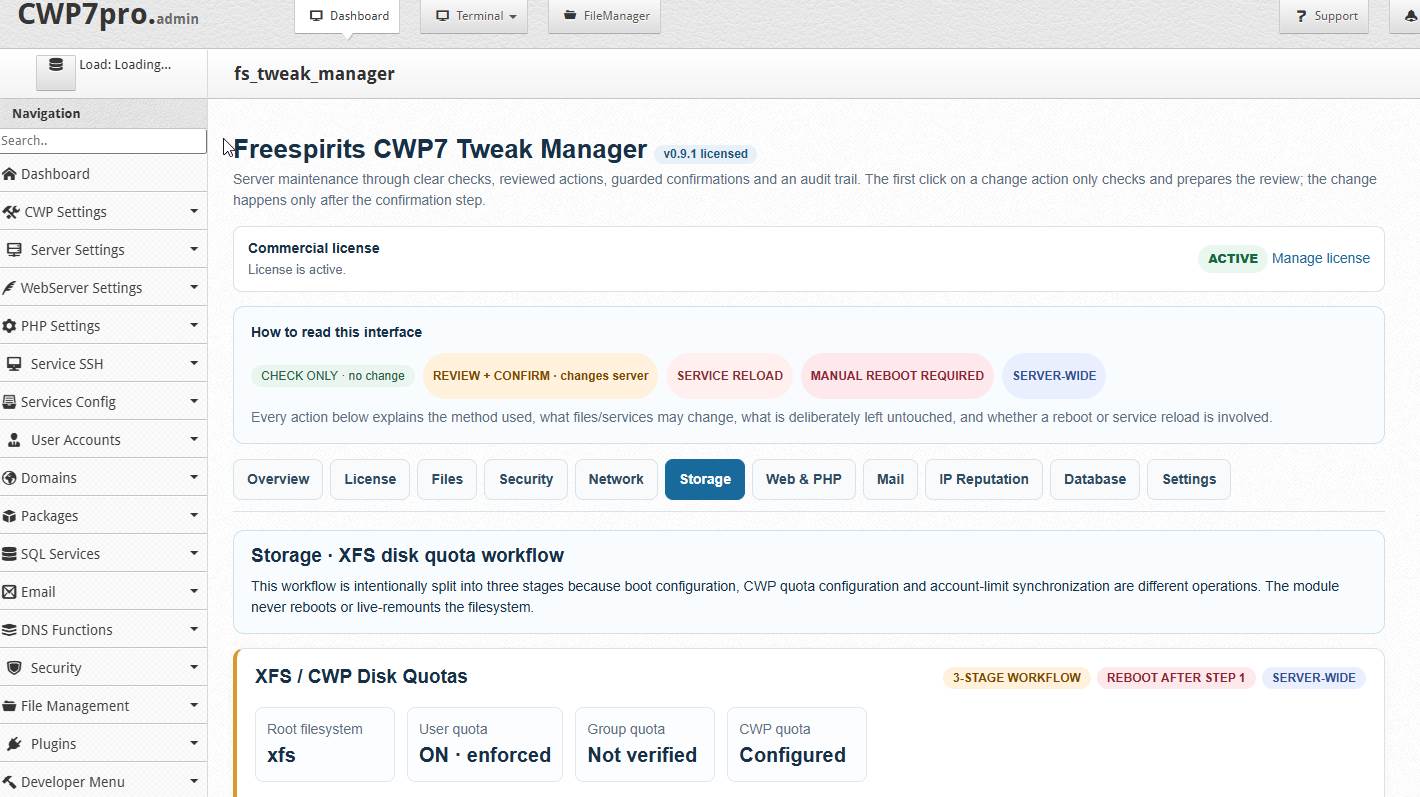
XFS quota configuration and CWP account quota synchronization.

⚡ Web & PHP

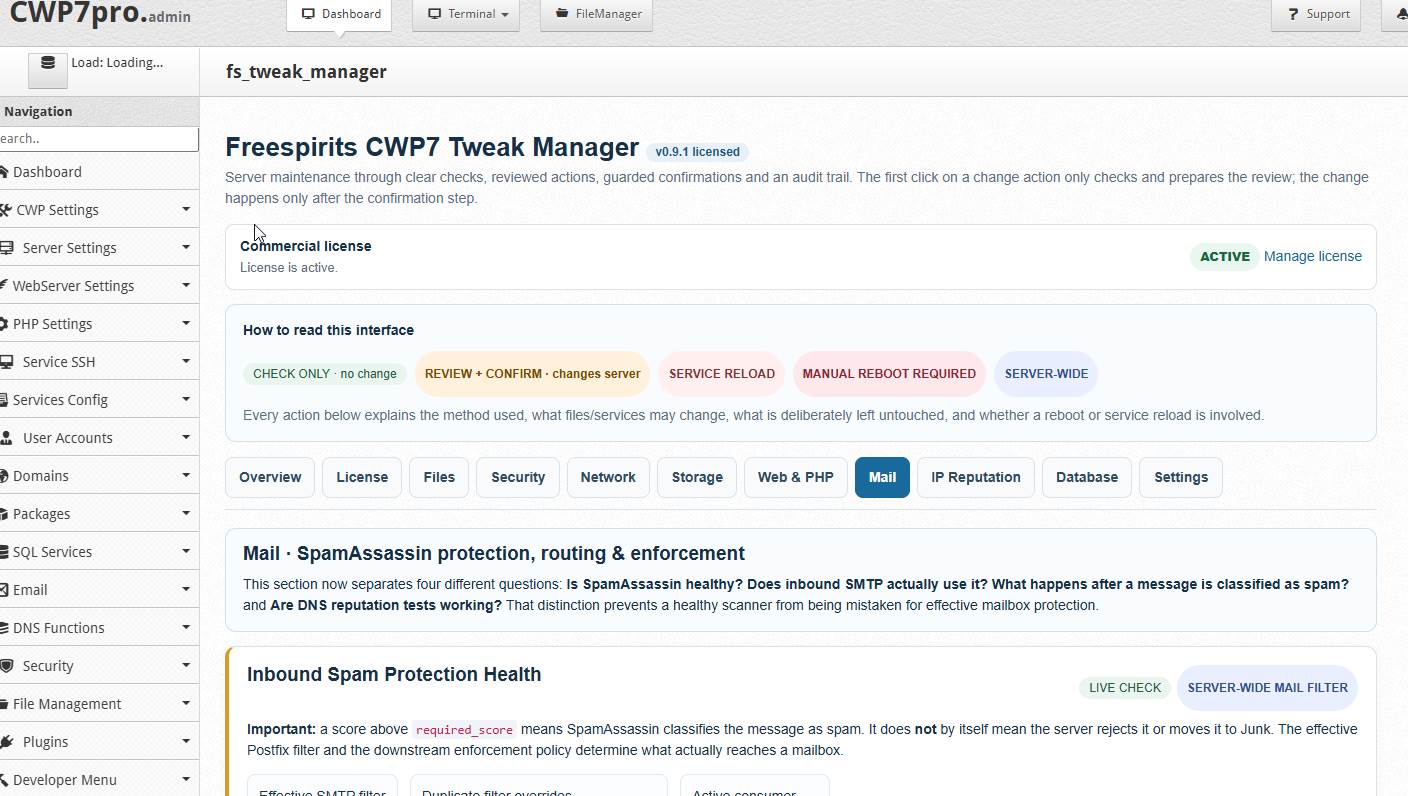
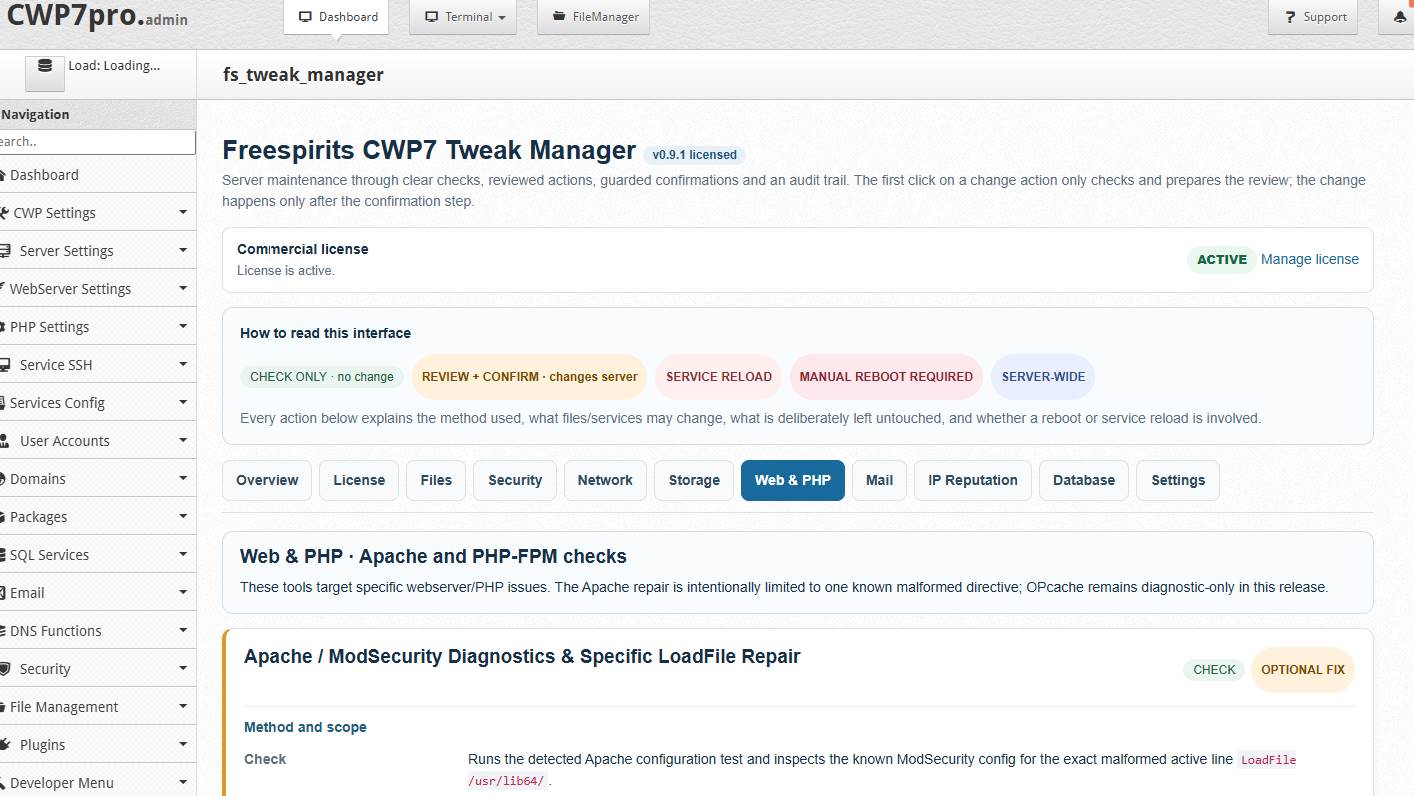
Apache diagnostics, configuration repair and PHP OPcache inspection.

✉ Mail

SpamAssassin health tests, mail pipeline detection, tuning and diagnostics.

📡 IP Reputation

Blacklist and reputation monitoring with automatic warning emails.

🗄 Database

Database and Roundcube readiness checks without dangerous blind database operations.

🔑 License

Integrated Freespirits servidor licensing, activation, validation and deactivation.

Intelligent Account Ownership & Permission Repair

One of the most common CWP7 problems happens when website files are copied,
extracted or uploaded as root.

Instead of belonging to the CWP account, website files may become:

root:root

This can result in 403 errors, PHP problems, WordPress update failures,
Joomla extension issues, cache errors, FTP problems and users being unable
to modify their own website files.

CWP7 Tweak Manager can safely inspect a selected account and normalize
the ownership and permissions of its website content.

  • Corrects root-owned website files under the selected account.
  • Corrects the account’s primary ownership and group where appropriate.
  • Sets normal directories to 0755.
  • Sets normal website files to 0644.
  • Protects symbolic links and hard-linked files.
  • Skips files belonging to another alojamiento cuenta.
  • Avoids crossing into unrelated mounted filesystems.
  • Preserves special treatment for sensitive files and executables.
  • Performs a second verification scan after the repair.
The module does not simply assume the operation succeeded.
It performs a post-check and reports whether any eligible ownership
or permission problems remain.

Smart CWP Hostname SSL Diagnostics

CWP hostname SSL problems can be frustrating because a valid certificate
may already exist while cwpsrv continues referencing an older certificate.

CWP7 Tweak Manager can inspect:

  • En servidor hostname.
  • The active hostname.bundle certificate.
  • Legacy hostname.crt references.
  • The hostname private key.
  • Certificate and key matching.
  • Certificate validity dates.
  • cwpsrv configuration syntax.
  • Certificates actually served on CWP ports.
  • Unexpected certificate references in active configuration files.

If everything is already correct, the module says so and removes the
unnecessary repair action.

If a genuine stale certificate reference is detected, the repair workflow
can back up the relevant configuration, make the minimal change, validate
cwpsrv, reload the service and retest the served certificate.

Smarter CSF & iptables Validation

Firewall maintenance is an area where blindly applying commands can be
dangerous. CWP7 Tweak Manager therefore separates package installation,
configuration repair and firewall reload into independent guarded steps.

The module understands that on AlmaLinux:

/sbin → /usr/sbin

It also resolves the actual executable behind iptables wrappers.
Therefore valid configurations such as:

/sbin/iptables → /usr/sbin/xtables-legacy-multi

are understood as valid aliases rather than incorrectly reported as
broken paths.

  • Checks whether iptables packages are installed.
  • Validates all six CSF iptables / ip6tables paths.
  • Resolves aliases and symbolic paths intelligently.
  • Checks ownership and executable safety.
  • Repairs only paths that genuinely need repair.
  • Keeps CSF reload as a separate guarded action.

IPv6 Management Through the GUI

CWP7 Tweak Manager can inspect both the running IPv6 state and the
configuration intended for the next boot.

It checks:

  • Whether IPv6 is enabled in the running kernel.
  • Whether IPv6 is disabled in installed boot entries.
  • Detected IPv6 addresses.
  • IPv4 availability before staging network changes.

The controls are state-aware. If IPv6 is already disabled, you are not
shown another meaningless Disable button. The available action becomes
Enable IPv6.

CWP7 Tweak Manager never automatically reboots the VPS.
Boot-related changes remain under the administrator’s control.

FTP over TLS Diagnostics

The module includes tools for diagnosing Pure-FTPd and Explicit FTPS.

  • Detect Pure-FTPd TLS configuration.
  • Check whether the TLS certificate exists.
  • Test standard FTP port 21.
  • Test custom ports such as 6477.
  • Check availability of the CWP Pure-FTPd TLS installer.
  • Run the CWP-provided TLS installation workflow when appropriate.

The module clearly distinguishes between enabling FTP TLS and configuring
a custom FTP listener or firewall rule.

XFS Disk Quota Management

Disk quotas on AlmaLinux/CWP require coordination between filesystem
mount options, boot parameters, XFS accounting and CWP account settings.

CWP7 Tweak Manager divides the procedure into three clear stages.

1 Enable XFS Quotas

The module checks the filesystem and mount layout, prepares the required
quota flags and safely stages the required boot parameters.

uquota,gquota,prjquota

2 Configure CWP

After reboot, the module verifies that XFS accounting and enforcement
really are active before configuring CWP’s quota type and partition.

3 Synchronize Existing Accounts

/scripts/cwp_api account update_diskquota_all

Existing CWP package and account disk limits can then be reapplied.

Advanced SpamAssassin Health & Protection

One of the most important recent additions to CWP7 Tweak Manager is the
advanced SpamAssassin diagnostic and management system.

Simply seeing that spamassassin.service is running does
not prove that incoming mail is actually passing through SpamAssassin.

Different CWP installations may use different mail pipelines such as:

Postfix → spamc / spamd

or:

Postfix → Amavis → SpamAssassin / ClamAV → Postfix

CWP7 Tweak Manager attempts to detect the real mail filtering path before
suggesting a repair.

Pipeline Detection

Detect Direct spamd, Amavis, Mixed or an unknown filtering path.

SpamAssassin Lint

Validate the active SpamAssassin configuration before making changes.

GTUBE Test

Use the standard SpamAssassin test message to prove spam detection works.

Bayes & Razor Diagnostics

Detect permission, lock and home-directory problems commonly seen on AlmaLinux.

GUI Spam Sensitivity Control

Administrators can adjust SpamAssassin sensitivity directly through
the module without manually editing configuration files.

5.0 Standard
4.5 Stronger
4.0 Aggressive
3.5 Very Aggressive

Optional subject tagging can also be enabled:

[***SPAM***]

Before applying a configuration change, CWP7 Tweak Manager backs up the
existing configuration, validates the new configuration and restores the
previous state if validation fails.

Analyze Suspicious Emails

When an obvious phishing or spam message reaches a mailbox, you can paste
its raw email source into CWP7 Tweak Manager.

The module can then tell you:

  • Whether the original message already contained SpamAssassin headers.
  • The score assigned by the servidor’s current SpamAssassin rules.
  • The active required spam threshold.
  • Whether the message would currently be classified as spam.
  • Which rules contributed to the result when available.
This helps distinguish between a message that bypassed SpamAssassin
completely and a message that was scanned but simply did not receive
a high enough score.

The pasted message is processed locally for analysis and is not intended
to be permanently stored by the module.

SpamAssassin Rule Updates

CWP7 Tweak Manager can run the official SpamAssassin rule updater:

sa-update

If new rules are available, the module validates the resulting
configuration and reloads the correct mail-filter service.

If no update is available, unnecessary service restarts are avoided.

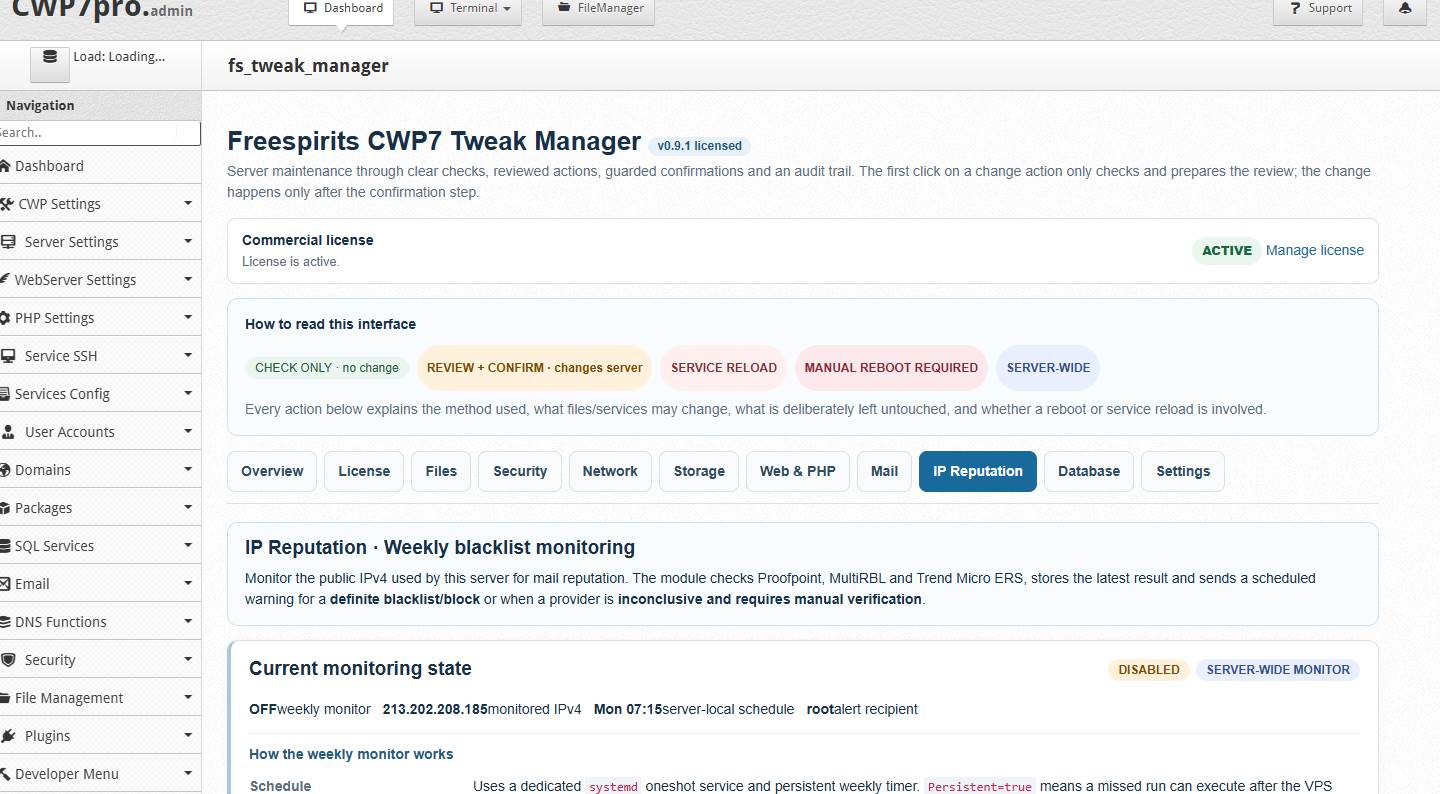
Weekly IP Reputation Monitoring

A correctly configured mail servidor can still suffer delivery problems
when its outbound IP develops a poor reputation.

CWP7 Tweak Manager integrates checks for:

  • Proofpoint IP Check
  • MultiRBL
  • Trend Micro Email Reputation Services

The result is classified as:

CLEAN
LISTED / BLOCKED
UNKNOWN / INCONCLUSIVE

An UNKNOWN response is deliberately not treated as CLEAN.

The module can also create an automatic weekly reputation check.
You choose:

  • The IP address to monitor.
  • The weekday.
  • The check time.
  • The administrator email address.
If a definite blacklist or block is detected, CWP7 Tweak Manager can
send an email warning automatically.

If a provider cannot return a reliable machine-readable result, the
module can instead warn the administrator that manual verification is required.

Web, Apache & PHP Diagnostics

CWP7 Tweak Manager also includes practical diagnostics for common
webserver and PHP problems.

  • Apache configuration checks.
  • Detection of known malformed ModSecurity LoadFile entries.
  • Guarded configuration repair.
  • Apache syntax validation.
  • PHP OPcache detection across installed CWP PHP-FPM versions.
  • OPcache configuration inspection.

The emphasis is always on detecting the real servidor state instead of
blindly applying generic performance settings.

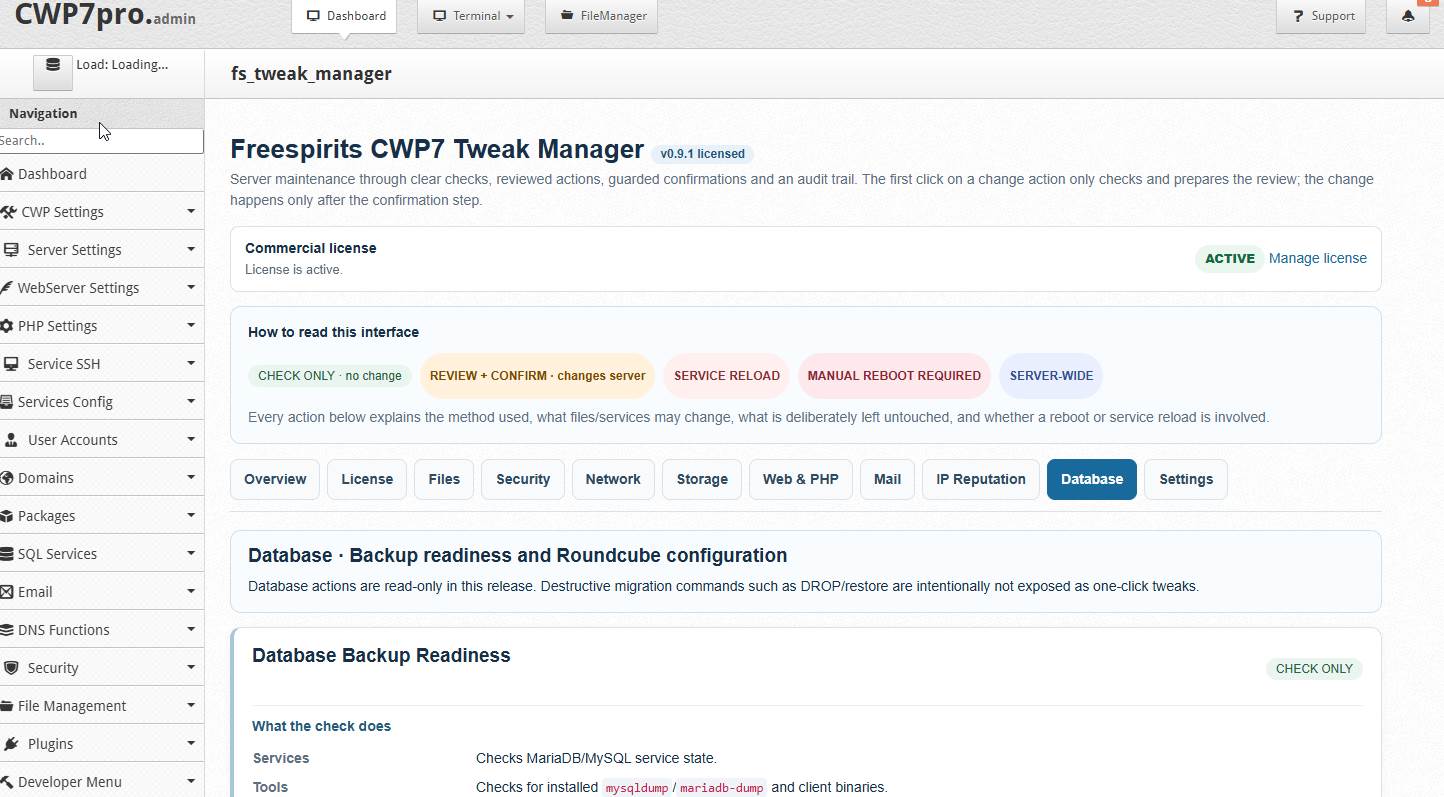
Database & Roundcube Diagnostics

The Database section provides useful read-only health information about
database and Roundcube components.

  • Database service readiness.
  • Backup utility availability.
  • Available disk capacity.
  • Roundcube configuration detection.
  • Relevant database configuration paths.

Destructive operations such as blindly dropping databases are deliberately
excluded from simple one-click repair workflows.

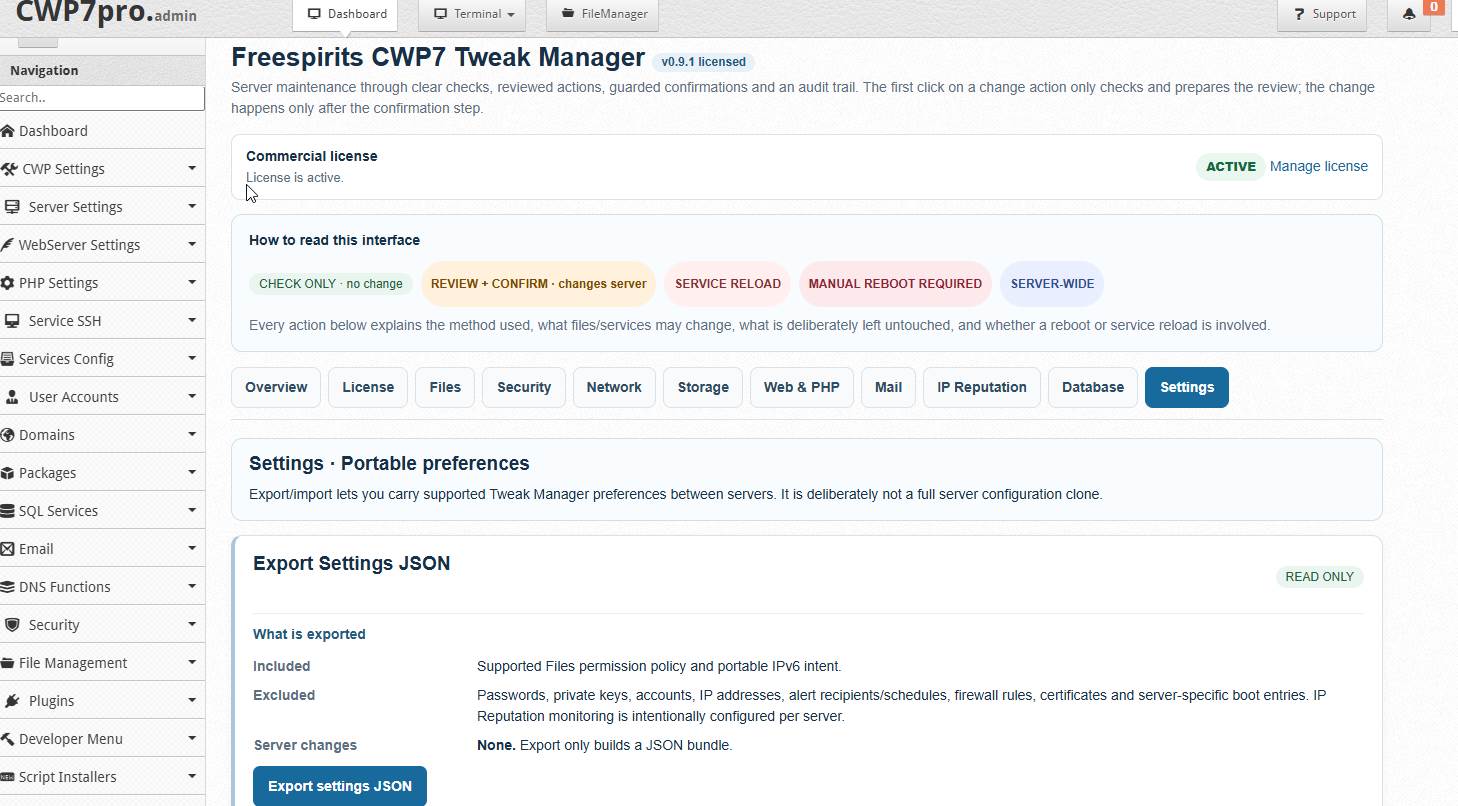
Portable Servidor Preferences

CWP7 Tweak Manager supports exporting selected module preferences into
a portable JSON configuration.

This can help administrators maintain a consistent preferred configuration
across multiple CWP servers.

Importing preferences does not blindly execute servidor changes.
Relevant actions must still be reviewed and confirmed on the destination servidor.

Integrated Commercial Licensing

CWP7 Tweak Manager includes integration with the Freespirits License Manager,
turning the module into a properly licensed commercial servidor product.

The License section supports:

  • License activation.
  • Immediate license validation.
  • Cached license state.
  • Grace-period handling.
  • Servidor-bound activation.
  • License deactivation.
  • Reusable activation slots according to the license policy.

The full license key is stored securely in a root-only file.

/var/lib/freespirits-tweak-manager/license.json

The module uses secure permissions and does not need to expose the
license key publicly inside the CWP interface.

Deactivating a license releases the activation from the current VPS
without uninstalling the module, removing servidor tweaks or deleting the license itself.

Diagnostics Still Available When Troubleshooting

Licensing has been designed practically.

Read-only diagnostics can remain available so administrators are not left
blind when troubleshooting a servidor.

Actions that modify servidor configuration require a valid license or a
permitted licensed grace state.

A State-Aware Interface That Understands the Servidor

One of the most important differences between CWP7 Tweak Manager and a
traditional collection of shell scripts is that the interface is designed
to react to the actual state of the servidor.

For example:

  • If IPv6 is already disabled, the module does not tell you to disable it again.
  • If XFS quotas are already active, the Enable button disappears.
  • If CSF paths are already valid, the Repair button disappears.
  • If the CWP hostname SSL configuration is correct, no unnecessary SSL repair is offered.
  • If iptables packages are installed, there is no reason to reinstall them.
  • If account ownership and permissions are already correct, no chmod/chown operation is proposed.
The goal is simple: if no action is necessary, the module should tell
you that everything is already correct instead of encouraging unnecessary changes.

Built for Real Alojamiento Administrators

CWP7 Tweak Manager is ideal for:

  • Web alojamiento providers.
  • Freelancers managing customer VPS servers.
  • Web design and development agencies.
  • System administrators.
  • WordPress and Joomla alojamiento providers.
  • Developers managing their own production infrastructure.
  • Administrators maintaining multiple CWP7 servers.

The more servers you maintain, the more valuable standardized and
repeatable maintenance procedures become.

Instead of remembering which command solved a problem six months ago,
the module explains the procedure directly in the administration interface.

Simple Installation & Upgrade Process

CWP7 Tweak Manager uses the same straightforward package format as other
Freespirits CWP modules.

Upload the module ZIP into:

/root/

Then install it using:

cd /root

rm -rf /root/cwp7-tweak-manager-v0.9.0

unzip -o /root/cwp7-tweak-manager-v0.9.0.zip -d /root/

cd /root/cwp7-tweak-manager-v0.9.0

chmod +x install.sh
bash install.sh

The installer is designed to recognize compatible previous versions,
back up existing module files and protect installations that appear to
have unknown local modifications.

Installing the Module Does Not Automatically Change Your Servidor

Simply installing CWP7 Tweak Manager does not automatically:

  • Change website ownership.
  • Change file permissions.
  • Disable IPv6.
  • Reload CSF.
  • Enable quotas.
  • Modify SpamAssassin.
  • Restart mail services.
  • Enable weekly reputation monitoring.
  • Reboot your VPS.

Servidor-changing actions remain under the administrator’s control.

En CWP7 Maintenance Toolkit We Always Wanted

SSH remains an essential part of professional servidor administration.
CWP7 Tweak Manager is not designed to replace SSH entirely.

Instead, it addresses the large number of recurring administration tasks
that do not need to be manually repeated every time.

Why search old forum posts, SSH history and personal notes whenever the
same issue returns?

Why blindly run a command before checking whether the servidor actually
needs the change?

Why continue displaying a Repair button after a problem has already been fixed?

CWP7 Tweak Manager combines your most frequently used CWP7 maintenance
workflows into one intelligent interface.

From website permissions and ownership to SSL, quotas, CSF, IPv6,
FTP TLS, SpamAssassin, PHP, databases and IP reputation monitoring,
the goal is to give administrators a single practical maintenance center.
⚙ CWP7 Tweak Manager

Diagnose faster. Repair smarter. Reduce repetitive SSH work.
Keep your CWP7 servers under control from one powerful administration interface.

Check → Review → Confirm → Apply → Verify

CWP7
AlmaLinux
Servidor Maintenance
Seguridad
Mail Protection
IP Reputation


Changelog

Freespirits CWP7 Tweak Manager — Changelog & Release Updates

Latest Version: v0.9.49 | October 2026

Smarter Servidor Management. Better Performance. Safer Automation.

Freespirits CWP7 Tweak Manager is a comprehensive servidor administration module designed for CWP7 and CWPpro environments. It brings important performance optimizations, security diagnostics, PHP management, email protection, firewall maintenance, and automated servidor health tools into one easy-to-use interface.

Every critical operation follows a safety-focused workflow:

Detect → Review → Confirm → Apply → Validate → Rollback if necessary


What’s New in v0.9.49 — Smart FastCGI Cache Management

This major update transforms the FastCGI Cache tab into a more intelligent, domain-aware caching management system.

1. Enable or Disable FastCGI Cache Per Domain

  • Select a supported website from the CWP control panel.
  • Detect whether FastCGI caching is available, enabled or disabled.
  • Enable anonymous-page caching through a reviewed GUI operation.
  • Disable configurations previously managed by Tweak Manager.
  • Preserve custom configurations and avoid unauthorized changes.

2. Intelligent Servidor and Domain Detection

  • Automatically inspect existing Nginx configurations.
  • Identify supported Nginx-to-PHP-FPM configurations.
  • Detect WordPress and Joomla document roots.
  • Recognize incompatible Apache/reverse-proxy architectures.
  • Block unsafe or ambiguous configurations instead of making speculative changes.

3. Conservative Cache Protection

  • Cache anonymous GET/HEAD requests with successful HTTP 200 responses for 30 seconds.
  • Bypass requests involving cookies, authorization, query strings, login areas and sensitive URLs.
  • Respect upstream cache-control behavior.
  • Exclude recognized dynamic commerce applications from automatic activation.

4. Automatic Domain Lifecycle Watchdog

  • Optional monitoring every five minutes.
  • Maintain approved cache configurations after supported CWP Nginx rebuilds.
  • Discover deleted domains and remove obsolete generated cache-zone references.
  • Reconcile missing or outdated generated configuration files.
  • Avoid deleting existing website cache data unnecessarily.

5. Legacy Configuration Compatibility

  • Support existing valid cache metadata zones, including 16 MB and 100 MB configurations.
  • Preserve compatible custom cache settings.
  • Detect legacy cache-generator cron jobs, including installations under /root/scripts/.
  • Safely migrate supported legacy cron entries when activating the new watchdog.

6. Protected Nginx Operations

  • Create private configuration backups.
  • Validate proposed changes using nginx -t.
  • Reload Nginx only when validation succeeds.
  • Restore previously working configuration when a managed operation fails.
  • Prevent concurrent managed reconciliation operations.

Important: FastCGI activation remains an explicit per-domain choice. Unsupported reverse-proxy configurations require a separate caching strategy.


v0.9.48 — FastCGI Cache Domain Lifecycle Watchdog

  • Introduced the dedicated FastCGI Cache management tab.
  • Added automatic discovery of supported cache-enabled domains.
  • Implemented removal of obsolete generated cache zones after domain deletion.
  • Added safe creation of missing cache directories for verified alojamiento accounts.
  • Added Nginx configuration validation, backups and rollback.
  • Introduced optional five-minute systemd watchdog monitoring.
  • Added controlled migration of supported legacy cache cron jobs.

v0.9.47 — PHP Workers Management

  • Introduced the dedicated PHP Workers tab.
  • Added alojamiento-account and PHP-FPM pool discovery.
  • Added four presets: Eco, Balanced, Busy and Peak.
  • Added per-account configuration previews and resource estimates.
  • Added guarded PHP-FPM configuration validation and graceful reload.
  • Added Restore Previous Settings and automatic rollback on failure.
  • Protected unrelated alojamiento accounts from accidental pool modifications.

v0.9.46 — Stable Mail Repair Confirmation

  • Fixed changing state fingerprints during ClamAV/Amavis Review → Confirm operations.
  • Excluded temporary diagnostic filenames from safety fingerprints.
  • Preserved validation of actual configuration, socket and group state.
  • Improved reliability of the Mail Wizard confirmation workflow.

v0.9.45 — Advanced ClamAV Access Repair

  • Added functional testing of minimal supplementary-group combinations.
  • Preserved existing Amavis group memberships during temporary access tests.
  • Improved compatibility with different CWP7 ClamAV socket permissions.
  • Added guarded group-membership repair and rollback.
  • Prevented unnecessary ClamAV restarts or insecure permission changes.

v0.9.44 — ClamAV Compatibility Engine

  • Improved detection of running ClamAV profiles.
  • Eliminated inappropriate fallback to legacy runtime-directory repairs.
  • Added real functional scans before proposing access changes.
  • Improved support for dedicated and shared ClamAV configurations.

v0.9.43 — Dynamic Mail Scanner Discovery

  • Added detection of the ClamAV configuration actually used by Amavis.
  • Introduced real scanning tests under the Amavis service account.
  • Added automatic discovery of running ClamAV profiles.
  • Improved compatibility with custom socket and configuration paths.

v0.9.42 — Amavis Routing and Group Access

  • Added shared ClamAV socket-access diagnostics.
  • Introduced reviewed Amavis group-membership and routing repair.
  • Added configuration verification and rollback.
  • Preserved healthy ClamAV daemon processes during repair.

v0.9.41 — ClamAV Socket Routing Repair

  • Fixed Amavis configurations pointing to nonexistent ClamAV sockets.
  • Added identification of working shared scanner configurations.
  • Introduced guarded routing repair from the GUI.
  • Improved post-repair functional verification.

v0.9.40 — Multi-PHP Runtime Diagnostics

  • Improved independent detection of PHP CLI and PHP-FPM runtimes.
  • Added detailed PHP runtime health and dependency diagnostics.
  • Introduced reviewed repair for supported missing shared-library loader dependencies.
  • Improved full-stack timezone management for multiple PHP versions.

v0.9.39 — IPv6 Mixed Kernel Management

  • Improved detection of stale and orphaned kernel boot entries.
  • Added reviewed IPv6 normalization across verified installed kernels.
  • Prevented modifications to unrelated rescue and provider-specific entries.
  • Preserved manual reboot requirements.

v0.9.38 — Legacy iptables State Verification

  • Fixed false failures when masked legacy iptables services remain active (exited).
  • Improved systemd service-state classification and safety validation.

v0.9.37 — Firewall Isolation Reliability

  • Improved detection of systemd masks on older AlmaLinux installations.
  • Added stronger verification of masked services.
  • Improved rollback behavior when CSF reload has not started.

v0.9.36 — CSF and iptables Compatibility

  • Fixed compatibility with AlmaLinux xtables-nft-multi executable aliases.
  • Improved CSF management-port verification.
  • Preserved trusted executable validation and firewall rollback safeguards.

v0.9.35 — Automatic Module Installation

  • Added optional unattended installation of verified updates.
  • Preserved Notify Only as the default.
  • Added signed-release authorization checks and a publisher-side automatic-install control.
  • Added installation locking, failure cooldowns, backup and rollback.
  • Added update success and failure notifications.

v0.9.34 — SELinux DNS Port Compatibility

  • Fixed false DNS-port conflicts on SELinux-disabled servers.
  • Preserved existing SELinux policy protections when applicable.

v0.9.33 — Advanced SpamAssassin DNS Port Discovery

  • Expanded alternative DNS listener port detection.
  • Avoided occupied and ephemeral TCP/UDP ports.
  • Improved SELinux compatibility reporting.
  • Preserved CWP/BIND DNS configuration.

v0.9.32 — Legacy iptables Isolation

  • Added detection of obsolete iptables service states.
  • Introduced reviewed isolation of stale firewall services.
  • Added CSF chain and management-port verification.
  • Added firewall backups and rollback safeguards.

v0.9.31 — MariaDB Timezone Alignment

  • Added detection of outdated MariaDB runtime timezone offsets.
  • Introduced guarded service restart only when necessary.
  • Preserved existing database records and timestamps.

v0.9.30 — Automatic Update Watch

  • Introduced configurable update monitoring.
  • Added Stable/Beta release channels.
  • Added customizable monitoring intervals and notification addresses.
  • Added update status reporting and test notifications.

v0.9.29 — Signed Update Compatibility

  • Improved Ed25519 signature verification on older AlmaLinux/RHEL environments.
  • Added multiple secure cryptographic verification backends.
  • Preserved strict signature and package-integrity requirements.

v0.9.28 — Database Connection Improvements

  • Fixed database query execution failures.
  • Improved detection of secure local MariaDB credentials.
  • Strengthened timezone and mail-account containment diagnostics.

v0.9.27 — Legacy OpenSSL Support

  • Added compatibility improvements for signed updates on OpenSSL 1.1.1.
  • Preserved strict cryptographic signature validation.

v0.9.26 — Full Stack Time Synchronization

  • Added synchronization of Linux, PHP and MariaDB/MySQL timezone settings.
  • Introduced managed PHP timezone configuration files.
  • Added PHP-FPM validation, backup and rollback.

v0.9.25 — Time & Zone Management

  • Introduced the dedicated Time & Zone tab.
  • Added servidor/browser timezone comparison.
  • Added chrony and NTP synchronization checks.
  • Introduced reviewed Linux timezone configuration.

v0.9.24 — IP Blacklist Recovery Center

  • Added blacklist and deliverability recovery shortcuts.
  • Integrated resources for AbuseIPDB, CleanTalk, Microsoft and Yahoo/AOL.
  • Improved visibility of the monitored servidor IP.

v0.9.23 — Mail Guard and Live DNSBL Monitoring

  • Improved compromised-mailbox containment diagnostics and retries.
  • Added live Spamhaus ZEN and SpamCop DNSBL checks.
  • Introduced hourly monitoring and listing/recovery notifications.
  • Improved email deliverability evidence and reporting.

v0.9.22 — Automatic Mailbox Containment

  • Added optional password rotation for critically compromised mailboxes.
  • Added emergency Direct MX administrator alerts.
  • Added incident-based containment controls and notification status.
  • Preserved incoming mailbox delivery.

v0.9.21 — SpamAssassin DNS Resolver Improvements

  • Improved Unbound resolver setup on SELinux-enforcing servers.
  • Added safer port-policy management.
  • Improved detection and repair of partial resolver installations.
  • Preserved CWP DNS services.

v0.9.20 — ClamAV Runtime Configuration Repair

  • Improved detection of conflicting local and vendor tmpfiles configurations.
  • Added precise runtime-directory repair and rollback safeguards.

v0.9.19 — ClamAV Recovery Compatibility

  • Improved compatibility with CWP package-managed tmpfiles rules.
  • Expanded guarded runtime repair eligibility.
  • Improved verification and service readiness handling.

v0.9.18 — Antivirus Runtime Health Checks

  • Added real ClamAV socket health checks to the Mail Wizard.
  • Introduced reviewed runtime-directory repairs.
  • Prevented dependent mail actions from proceeding when antivirus verification fails.

v0.9.17 — License and Update Entitlement Improvements

  • Added compatibility with Freespirits License Manager update entitlements.
  • Separated commercial license validity from update-access status.
  • Improved license and update information displayed in the GUI.

v0.9.16 — Outbound Mail Guard Foundation

  • Introduced lightweight outbound mail monitoring and related mail-abuse controls.

Safe Servidor Maintenance by Design

Freespirits CWP7 Tweak Manager emphasizes controlled, transparent operations instead of blind configuration changes.

Key safeguards include:

  • Read-only diagnostics before changes.
  • Explicit review and administrator confirmation.
  • Narrowly scoped operations.
  • Configuration validation.
  • Private backups.
  • Post-operation verification.
  • Automatic rollback where supported.
  • Protection against ambiguous or unsupported servidor configurations.

Freespirits CWP7 Tweak Manager — One control panel. More control. Safer servidor optimization.

Compatibility and available actions depend on the installed CWP, operating-system, service and application configuration. Always review proposed production changes before confirming them.

Latest Changes

v0.9.91

Bugfix

Fixed the Website File Lockdown error “Invalid recorded website-relative path” caused by legitimate Greek, Unicode and space-containing filenames. Preserved secure filesystem traversal, original ownership, existing lockdown records, individual folder actions, and all four writable-folder policies: Normal, Recommended, Strict and Custom.

v0.9.90

Bugfix

All four policies remain visible: Normal, Recommended, Strict and Custom.
Whole-website Lock and Restore remain available.
Protected folders and writable exceptions are shown in the read-only report. Protected folders are paginated, so large lists can be browsed without silently truncating them.
Individual folder Re-lock and Restore retain their review-and-confirm procedure.
Already safely protected root:root objects are preserved without unnecessary ownership changes.
Helper failures now report more useful diagnostic information rather than incorrectly suggesting sudo is always the cause.

v0.9.89

Bugfix

Simplified Website File Lockdown management with dedicated recursive folder re-lock and permission-restoration actions, inline review and error feedback, direct re-lock controls for saved writable exceptions, and advanced website-level controls moved into a separate expandable section. Preserved existing lockdown records, original permission metadata, and mandatory review-and-confirm safeguards.

v0.9.88

Major

What's new
- Selectable writable defaults: Choose CMS-compatible, runtime-only, strict, or custom exceptions when locking a website.
- Recursive folder restoration: Restore account permissions for a single folder, including existing files and subfolders, without unlocking the rest of the website.
- Works with existing exceptions: You can repair images/stories/works even when the broader images directory is already excluded.
- Individual exception re-locking: Re-lock an entire saved exception without restoring and locking the entire website again.
- Preserved configurations: Existing lockdown records, exceptions and protected files remain unchanged during the upgrade.
- Safety checks: Preview and confirmation before changes, with protection against unsafe symlinks, mounts and unknown file ownership.

v0.9.87

Minor

What's fixed
Added a dedicated read-only Website File Lockdown report inside the CWP7 Tweak Manager GUI, displaying stored writable exceptions, filesystem existence, ownership and permissions, and potential access problems without requiring administrators to inspect private JSON files manually. Preserved existing lockdown, restoration and exception-management safeguards, with new regression coverage.

v0.9.86

Seguridad

What's Fixed
Enhanced Website File Lockdown with the ability to add additional writable files and directories after a Joomla, WordPress or custom website has already been secured, without unlocking the entire installation. Introduced a dedicated GUI-based Add Writable Exceptions workflow with support for deeply nested application directories, individual files, read-only previews and administrator confirmation. The module now selectively restores the original recorded ownership and permissions of approved paths while keeping all other application files protected. Added automatic lockdown-record updates, restoration consistency checks, filesystem safety validation, stale-review protection and interrupted-operation recovery. Improved compatibility with gallery thumbnail directories, application-generated caches and other custom writable locations. Preserved existing module security features, licensing, PHP-FPM management and backward-compatible update functionality.

v0.9.85

Minor

What's Fixed
Introduced Website File Lockdown, a new standalone security feature integrated into CWP7 Tweak Manager. Administrators can selectively protect Joomla, WordPress and supported custom websites by changing application-code ownership to root while preserving essential writable directories such as cache, tmp, temp, logs, administrator/cache, images and WordPress uploads under the hosting account. Added automatic CMS detection, configurable writable exceptions, read-only security previews, explicit administrator confirmation, original ownership and permission restoration, and safeguards against symlinks, hardlinks, unsafe filesystem layouts and overlapping website protections. Integrated lockdown awareness with the existing Files permission-repair functionality to prevent accidental removal of active protection. Preserved existing Redis, Memcached, PHP-FPM, FastCGI, licensing and backward-compatible update functionality.

v0.9.84

Bugfix

What's Fixed
Fixed automatic upgrade compatibility between legacy and modern Freespirits CWP7 Tweak Manager versions. Resolved an issue where older updaters could incorrectly reject a successfully installed release because of changes in the GUI version-display format, triggering unnecessary rollback operations. Introduced backward-compatible version recognition for v0.9.55–v0.9.69 while retaining the modern structured version, SHA-256 integrity and installation-manifest verification used by newer releases. Improved the installer to recognize existing v0.9.83 installations and preserved all existing security checks, administrator settings, licensing, Redis and Memcached management, PHP-FPM functionality, FastCGI monitoring, backups and rollback protection. Designed for centralized signed-update distribution across mixed CWP7 installations on supported AlmaLinux servers.

v0.9.83

Minor

What's Fixed
Improved Redis and Memcached PHP-FPM extension activation and verification following successful installation. Added direct PHP-FPM reload review from cache connection results, runtime-specific master-process extension detection, independently approved graceful reloads, and immediate private PHP-FPM verification. Corrected misleading success reporting so that a service reload is never confused with confirmed extension activation. Enhanced FastCGI Cache Manager with read-only auditing of independently managed monthly zone generators and five-minute health guards, including script integrity, scheduled automation discovery, Bash syntax validation and Nginx configuration checks. Improved GUI status reporting for externally managed caching while preserving existing cron jobs, cache directories, Redis and Memcached services, PHP configuration, licensing and rollback safeguards.

v0.9.82

Major

What's Fixed
Fixed Redis Manager's false active-job and ownership warnings caused by valid Redis configuration backups exceeding the module's internal state-file size limit. Introduced bounded rollback validation, preserved historical recovery data, and restored eligible Redis PHP-extension management operations. Expanded the PHP Redis and Memcached extension manager to support verified extension directives in existing main php.ini configurations, with administrator approval, private backups, exact-line modification, configuration fingerprint protection, validation and safe error recovery. Extended external-extension review beyond PHP 8.3 and improved FastCGI Cache visibility for installations using existing independent zone generators and health guards. Preserved working server configurations, service safeguards, licensing, existing cron automation and backup protection.

v0.9.81

Major

What's Fixed
Introduced investigation-driven compatibility improvements for CWP7 Tweak Manager, addressing real server configurations identified on AlmaLinux 9.8. Corrected Redis configuration detection to recognize verified RPM-managed ownership and permissions without requiring unnecessary ownership changes. Improved localhost security validation, including support for Redis's optional IPv6 loopback binding syntax, while preserving strict checks for untrusted configurations. Enhanced Redis configuration updates and rollback to retain verified package ownership. Improved FastCGI Cache Manager discovery to recognize independently managed cache zones, scheduled generators, and health-repair services without creating conflicting automation or modifying working configurations. Clarified the PHP Settings Editor's review and confirmation process while preserving version-specific settings, PHP-FPM safeguards, existing Memcached functionality, PHP Workers reporting, licensing, update integrity, and rollback protection.

v0.9.80

Bugfix

What's Fixed
Improved Redis PHP extension compatibility and management across supported AlmaLinux 8 and 9 CWP7 installations. Fixed overly restrictive Redis Manager checks that previously prevented administrators from building or enabling PHP Redis extensions when an otherwise operational Redis server used a nonstandard configuration directory. Separated verified live Redis connectivity and protected-mode checks from server configuration ownership requirements, allowing secure per-version PHP extension management without unnecessary Redis service modifications. Enhanced Redis configuration discovery, preserved strict safeguards for protected configuration files, and improved cache connection reporting to distinguish missing PHP extensions from PHP-FPM services awaiting reload. Added clearer GUI guidance and regression coverage while preserving existing Memcached functionality, PHP version isolation, licensing, configuration protection, and reviewed server operations.

v0.9.79

Major

What's Fixed
Improved Redis and Memcached management compatibility across different AlmaLinux and CWP7 server configurations. Enhanced Redis diagnostics to identify configuration directory ownership and permission problems, introduced a secure, administrator-approved ownership repair for eligible RPM-managed Redis installations, and separated live cache-service verification from PHP extension management to reduce unnecessary configuration-related blocks. Expanded the PHP Workers section with detailed live worker counts, account-level and PHP-version capacity summaries, configured worker limits, and available headroom. Improved CWP form-security feedback with clearer recovery instructions for expired browser-context tokens. Preserved existing security restrictions, server configuration backups, licensing, cache memory settings, and production service protections.

v0.9.78

Bugfix

What's Fixed
Fixed the FastCGI Cache Manager's configuration discovery dead end when existing Nginx cache-zone files lack a recognized generated-file signature. Introduced intelligent, read-only inspection of existing FastCGI zones, including configuration ownership, permissions, associated domains, and detailed compatibility diagnostics. Added a secure, administrator-approved adoption workflow for verified legacy configurations, featuring fingerprint validation, root-private backups, Nginx syntax checks, automatic restoration on validation failure, and improved GUI guidance. Existing cache definitions, application configurations, and website caching behavior remain preserved. Unknown or conflicting configurations continue to be protected against unauthorized changes, improving reliability and compatibility with existing CWP7 Nginx installations.

v0.9.77

Minor

What's Fixed
Fixed the Memcached Manager configuration detection that previously blocked administrators with a generic “Custom Memcached configuration detected” warning. Introduced intelligent configuration inspection, support for common nonstandard configuration formats, detailed before-and-after comparisons, and a new GUI-based Review & Confirm workflow for safely standardizing existing Memcached installations. Added explicit approval for replacing custom directives, protected configuration backups, fingerprint verification, rollback safeguards, and post-configuration service health checks. Improved compatibility with existing AlmaLinux/CWP installations while preserving localhost-only security, disabled UDP access, PHP extension management, and all other existing Tweak Manager functionality.

v0.9.76

Minor

What's Fixed
Fixed the PHP Settings Editor's save verification so valid PHP-FPM timeout settings are no longer rejected because PHP CLI reports hardcoded max_execution_time=0 and max_input_time=-1. Added independent verification of the exact managed PHP INI file, PHP INI scan loading, applicable CLI settings, and PHP-FPM configuration, while keeping live website settings explicitly unverified until tested. Improved the per-version GUI with visible saved overrides, safer 120-second initial timeout suggestions, automatic navigation to the Review & Confirm panel, and clear post-save confirmation. Preserved rollback protections, version-specific scope, optional PHP-FPM reloads, cache managers, server monitoring, licensing, and all other existing functions.

v0.9.75

Minor

Introduced a comprehensive Verify All Cache Connections feature for Redis and Memcached, performing automated write, read and delete verification across detected PHP-FPM versions, with independent PHP CLI and private PHP-FPM FastCGI connection results. Added secure management of pre-existing PHP 8.3 Redis and Memcached extensions, allowing administrators to review, disable and restore verified extension-only INI configurations directly through the GUI. Implemented exact configuration backups, state fingerprint validation, automatic recovery after failed changes, separately confirmed PHP-FPM reloads, and improved verification reporting. All existing PHP extensions, cache memory settings, server services, licensing functionality and other CWP7 Tweak Manager features remain preserved.

v0.9.74

Minor

What's Fixed
Fixed the Redis PHP extension source-extraction workflow to support the standard PECL archive structure, allowing PHP 7.4 and other compatible PHP versions to proceed to compilation while preserving checksum verification, archive security checks, and PHP ABI compatibility validation. Improved Redis installation reporting with detailed build stages, progress tracking, and explicit success or failure results. Enhanced PHP Workers monitoring with real-time process discovery and verified spawned worker counts per hosting account and PHP-FPM version, distinguishing actual processes from configured worker limits. Improved the Time & Zone interface to clearly separate System CLI PHP installations from PHP-FPM runtimes, eliminating confusing duplicate-version labels. All existing security protections, module licensing, configuration management, and reviewed server actions are preserved.

v0.9.73

Minor

What's Fixed
Improved PHP-FPM worker monitoring to distinguish configured pools from actively running workers, preventing misleading resource usage reports. Enhanced the Per-Version PHP Settings Editor with highlighted current values, documented PHP defaults, recommended performance profiles, and a clearer Review & Save workflow. Improved PHP 8.5 detection to hide unavailable repair options automatically. Fixed the PHP 7.4 Memcached installation failure caused by overly restrictive PECL archive validation, while preserving essential security checks and PHP compatibility protections. Additional interface refinements improve usability, configuration clarity, and overall server management reliability.

v0.9.72

Bugfix

Update success displayed in red when notification failed. Separates installation success from notification failure
Background job accepted as completed. Clearly reports queued, running, completed or failed
PHP 7.4 build stays unverified. Displays build stage and final outcome
Generic compilation failure. Reports the failed stage and a bounded diagnostic
Repeated build submissions. Blocks overlapping Memcached actions
No convenient progress tracking. Automatically refreshes running-job status
PHP-FPM not reloaded. Explicit separate reload remains required

v0.9.71

Minor

Feature v0.9.71
Redis / Memcached service health Preserved
Stop & Disable at Boot New GUI action
Start & Enable at Boot New GUI action
Separate reviewed confirmation Included
Legacy Redis rollback errors Isolated from new actions
Existing Redis rollback.json Preserved, not deleted
New managed Redis rollback record Separate trusted file
Per-version PHP extension management Preserved
Service verification and auditing Included
Installer compatibility with v0.9.70

v0.9.69

Bugfix

Improving Redis for higher PHP versions

v0.9.68

Bugfix

New package addressing the PHP extension diagnostics and Redis manager-state problem.

v0.9.67

Bugfix

Redis enable engine improvements

v0.9.66

Bugfix

What's fixed
- Redis ownership repair: Uses verified file-descriptor operations compatible with Linux.
- Safer rollback: Restores original ownership and permissions if a later verification fails.
- Clearer separation: Memcached and Redis have distinct panels, accent borders and spacing.
- Visible confirmation: The Redis ownership confirmation appears directly below Step 1A, not at the bottom of the PHP extensions table.
- Memory controls: Explains why the 512 MB action is disabled until Redis's configuration passes verification.
- Action results: Displays completion or failure feedback in the relevant cache section.

v0.9.65

Bugfix

What's fixed
- GUI ownership repair: Detects when Redis owns /etc/redis.conf and offers a reviewed change to root:redis with mode 0640, only after verifying the service account, RPM ownership and file safety.
- 512 MB memory change: Allows an explicitly approved reduction from 1024 MB when Redis's live and saved settings agree.
- Rollback: Independent rollback for the ownership change.
- Safer configuration updates: Preserves file group ownership during Redis configuration changes.
- No unnecessary actions: Ownership repair doesn't restart Redis or modify its keys.

v0.9.64

Bugfix

What v0.9.64 fixes
- Corrects Redis localhost listener detection from ss output.
- Displays the real /etc/redis.conf path rather than substituting an incorrect path after an error.
- Reports exact configuration-file ownership, permissions and validation failures.
- Checks the running Redis process's configuration location.
- Retrieves permitted, non-sensitive effective security and memory settings.
- Recognizes existing 1 GB Redis memory allocations.
- Displays a green status for verified localhost connectivity independently of unresolved configuration checks.
- Preserves the fail-closed security controls and existing PHP extension installations.

v0.9.63

Bugfix

Step 1 — Cache server
Installed, running, secured and responding, with the actual configured memory limit displayed.

Step 2 — Selected PHP extension
Show loaded version, ABI compatibility, exact INI location and whether any action is needed.

Step 3 — Connection and PHP-FPM verification
Verify the selected PHP runtime and actual cache connection; distinguish CLI success from PHP-FPM web-request verification.
Completed steps should receive a light-green background. Unnecessary action buttons should be disabled, while unverified conditions should remain clearly marked rather than displayed as successes.

v0.9.62

Major

New Web & PHP → Cache Server & PHP Extension Manager
Two independent sections: Memcached Manager and Redis Manager.
Each provides safe read-only status checks; a separately reviewed service installation/hardening action; a table of verified PHP-FPM versions; per-PHP extension ABI and CLI checks; review/enable/disable, optional pinned source build, independently approved selected PHP-FPM reload; per-service root-private undo and recorded job status.

v0.9.61

Bugfix

What's fixed
- max_input_time = -1 is now accepted as PHP's valid inherited/default value.
- max_execution_time = 0 is accepted, with a warning that applying it to PHP-FPM disables the execution-time limit.
- An additional confirmation is required before applying unlimited timeouts.
- Invalid submissions preserve the values you entered.
- The existing 600-second suggested profile remains available.
- All other Tweak Manager features are preserved.
The official PHP documentation confirms both special values

v0.9.60

Minor

New: Web & PHP → Per-Version PHP Settings Editor
The GUI automatically discovers verified PHP-FPM installations, including PHP 7.4, 8.1, 8.3 and 8.5 where installed.
It displays the current effective values for each PHP version and lets you edit them independently.
PHP setting Your suggested profile
expose_php Off
max_execution_time 600
max_input_time 600
max_input_vars 3000
memory_limit 2048M
post_max_size 128M
upload_max_filesize 128M
default_socket_timeout 300

v0.9.59

Minor

What's new in v0.9.59
1. Safe Server Log Discovery
Detects supported system, Apache, Nginx, PHP-FPM, WordPress, Joomla and CWP module logs. Reports disk usage, ages, file counts, exclusions and large active logs. Scans are bounded to avoid unnecessary server I/O.

2. Verified Historical Log Cleanup
Default 30-day retention with Preview → Confirm → Apply & Verify. Only qualifying historical rotated files are eligible. File fingerprints, ownership, open handles, mount boundaries and permissions are rechecked before deletion.

3. Oversized Active Log Management
Default warning threshold: 250 MB. Reports growth between scans and bounded error-marker samples. Adds separately confirmed native Nginx rotation where all compatibility checks pass. Other active logs remain protected.

4. Optional Daily Automatic Cleanup
Root-owned systemd service and timer with scheduling jitter, locking, resource guards and configurable limits. Disabled by default. No automatic journal vacuum or active-log rotation.

5. Protection, Auditing & Rollback
Permanent backup exclusions, protected path rules, root-private action history, cleanup verification, reviewed settings changes and rollback of managed timer configuration.

v0.9.58

Bugfix

What's corrected
- AlmaLinux 8 compatibility: Recognizes the trusted /lib64 and /usr/lib64 library paths.
- Accurate PHP-FPM detection: A working service no longer fails the health check solely because its direct CLI has a PCRE2 conflict.
- Better error explanations: If PHP-FPM configuration validation genuinely fails, the GUI shows the actual reason.
- Direct timezone repair: Links to the PHP 8.5 repair action directly from Time & Zone.
- Safe upgrade: Recognizes v0.9.57 and preserves existing settings, licensing, backup and repair functionality.

v0.9.57

Minor

What's improved
- PCRE2 diagnosis: Detects the default and verified PCRE2 library paths, embedded PHP RUNPATH, and existing service repair.
- CLI repair: Preserves the existing php85-safe launcher and offers the managed PHP 8.5 CLI workaround through the GUI.
- PHP-FPM health: Separates CLI startup failures from PHP-FPM service and configuration health.
- Independent timezone fix: Aligns PHP 8.5 with the server's timezone without changing Linux, MariaDB or other PHP runtimes.
- Safe one-click workflow: Review, confirm, back up, apply, validate and undo the timezone repair from the CWP interface.
- Existing features preserved: Including the PHP 8.5.9–8.5.12 checksum-pinned mbstring source builder.

v0.9.55

Bugfix

The Updates tab now appears separately, next to License.
Tab Features
License Activate, validate, change or release your server license
Updates Check for releases, install signed updates, configure automatic updates and notifications
Settings Export and import supported preferences
The new Updates tab includes manual Check for Updates, Stable/Beta channel selection, release notes, reviewed installation, Automatic Update Watch, Notify Only or Auto-install mode, scheduling every 1–168 hours, email alerts, and update status.

v0.9.54

Bugfix

Under Web & PHP, there's a new section called Build Missing mbstring from Official PHP Source.

It provides the following workflow:
1. Detect: Check PHP 8.5.12, its API, missing mbstring module and compilation prerequisites.
2. Review: Display the exact files, PHP runtime and service that would be affected.
3. Build: After confirmation, download the official PHP source, verify its SHA-256 and compile the matching extension.
4. Verify: Test mbstring, validate PHP-FPM 8.5, restart only its service and attempt rollback if validation fails.

v0.9.53

Minor

New feature: Account Cron Jobs
You can now select a CWP7 hosting account and manage its scheduled tasks directly from Tweak Manager.
- Select account: Discover existing CWP hosting users.
- Load cron jobs: Read the account's actual crontab.
- Edit schedules: Add, modify, disable or remove individual cron entries.
- Preserve permissions: Jobs remain assigned to their original Unix account, not root.
- Review changes: See the exact differences before confirming.
- Automatic backup: Save the previous crontab privately before making changes.
- Verify installation: Read the saved crontab back and confirm it matches.

v0.9.52

Bugfix

What's fixed
The PHP 8.5 mbstring checker now:
- Reuses a verified PHP-FPM service library environment when available.
- Recognizes the specific PCRE2 startup failure and tests the already-trusted system PCRE2 path.
- Continues checking mbstring after PHP starts successfully.
- Reports whether mbstring is loaded, missing or incompatible.
- Uses the verified environment during any eligible reviewed repair.
- Preserves your existing PCRE2 fix and all other Tweak Manager features.