Περιγραφή
CWP7 Resource Shield
Διακομιστής-Level Attack Detection, Resource Protection & Automated Cloudflare Defense
Protect the διακομιστής — not just one website. Detect coordinated malicious traffic, identify abusive networks and stop confirmed threats before they repeatedly consume PHP, CPU, RAM and database resources.
Why Resource Shield Belongs on a Serious CWP7 Διακομιστής
When one website on a shared διακομιστής comes under attack, the problem rarely stays isolated to that website.
Repeated requests against WordPress login pages, XML-RPC, WooCommerce endpoints, PHP scripts and other expensive URLs can trigger PHP-FPM workers, database queries, plugins, cron jobs and background processes.
Eventually, one compromised or heavily attacked website can begin consuming resources needed by every other customer hosted on the same διακομιστής.
CWP7 Resource Shield is designed to intervene before abusive traffic becomes a διακομιστής-wide resource problem.
The Problem Traditional Website Security Does Not Fully Solve
Imagine φιλοξενία 20, 50 or 100 websites on a CWP7 διακομιστής.
One WordPress or WooCommerce website suddenly receives hundreds or thousands of automated requests targeting sensitive endpoints:
/wp-login.php
/xmlrpc.php
/wp-cron.php
The requests may originate from dozens of different IP addresses and appear individually insignificant.
But many of those IP addresses may belong to the same attacking network.
Without διακομιστής-level intelligence, malicious traffic can continue travelling through your infrastructure until expensive application layers begin processing it.
Once PHP is processing the request, διακομιστής resources are already being consumed.
Resource Shield Changes Where the Battle Happens
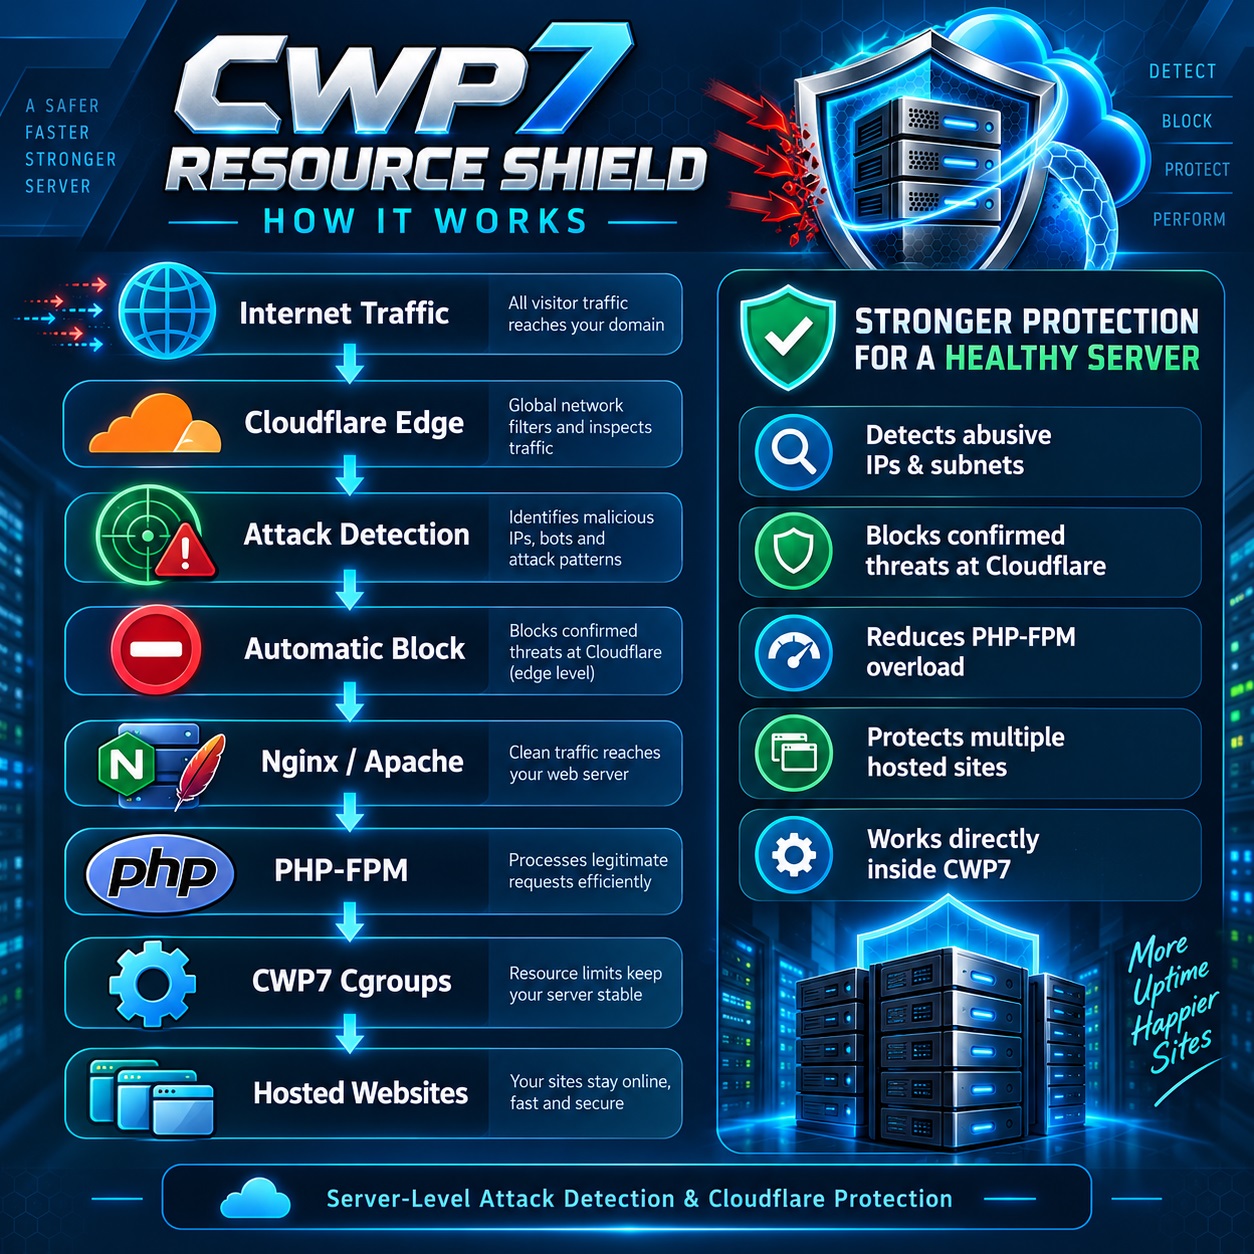
CWP7 Resource Shield continuously analyses relevant διακομιστής traffic and looks for suspicious and coordinated attack behaviour.
When configured protection criteria are met, the module can push a block outward to Cloudflare.
Instead of repeatedly allowing the same malicious network to reach Nginx, Apache, PHP-FPM, WordPress and MySQL, confirmed attack traffic can be rejected at Cloudflare’s edge.
One Module. Διακομιστής-Wide Visibility.
🛡 Διακομιστής-Level Protection
Unlike a WordPress security plugin that sees only one installation, Resource Shield operates at the CWP7 διακομιστής level and can monitor activity affecting multiple hosted domains.
☁ Cloudflare Defense
Confirmed malicious IP addresses or networks can be blocked through Cloudflare so subsequent traffic can be stopped before it reaches expensive application layers.
⚡ Resource Protection
Reducing abusive PHP requests helps protect PHP-FPM capacity, CPU, RAM and database resources that legitimate visitors and customers need.
🌐 Network Intelligence
Resource Shield can recognise coordinated behaviour across multiple addresses instead of treating every attacking IP as an unrelated event.
🖥 Native CWP7 Interface
Access Resource Shield directly from the Control Web Panel administrator interface without managing separate WordPress dashboards.
🔗 Multi-Διακομιστής Ready
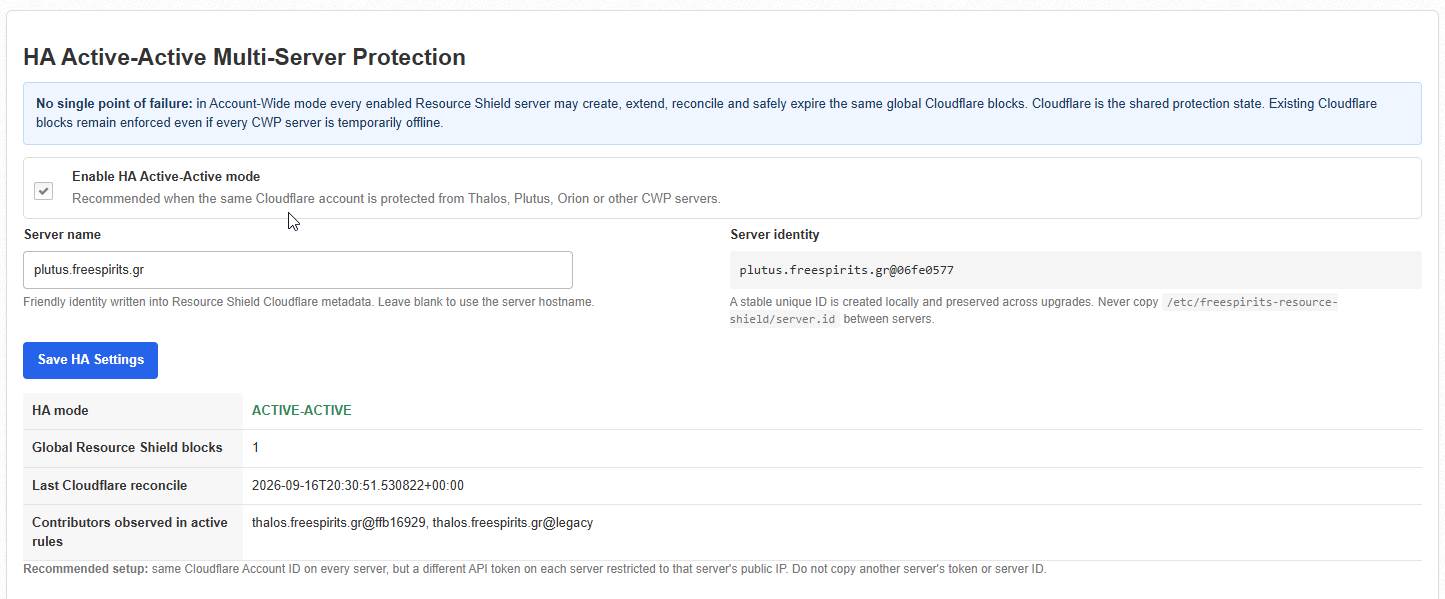
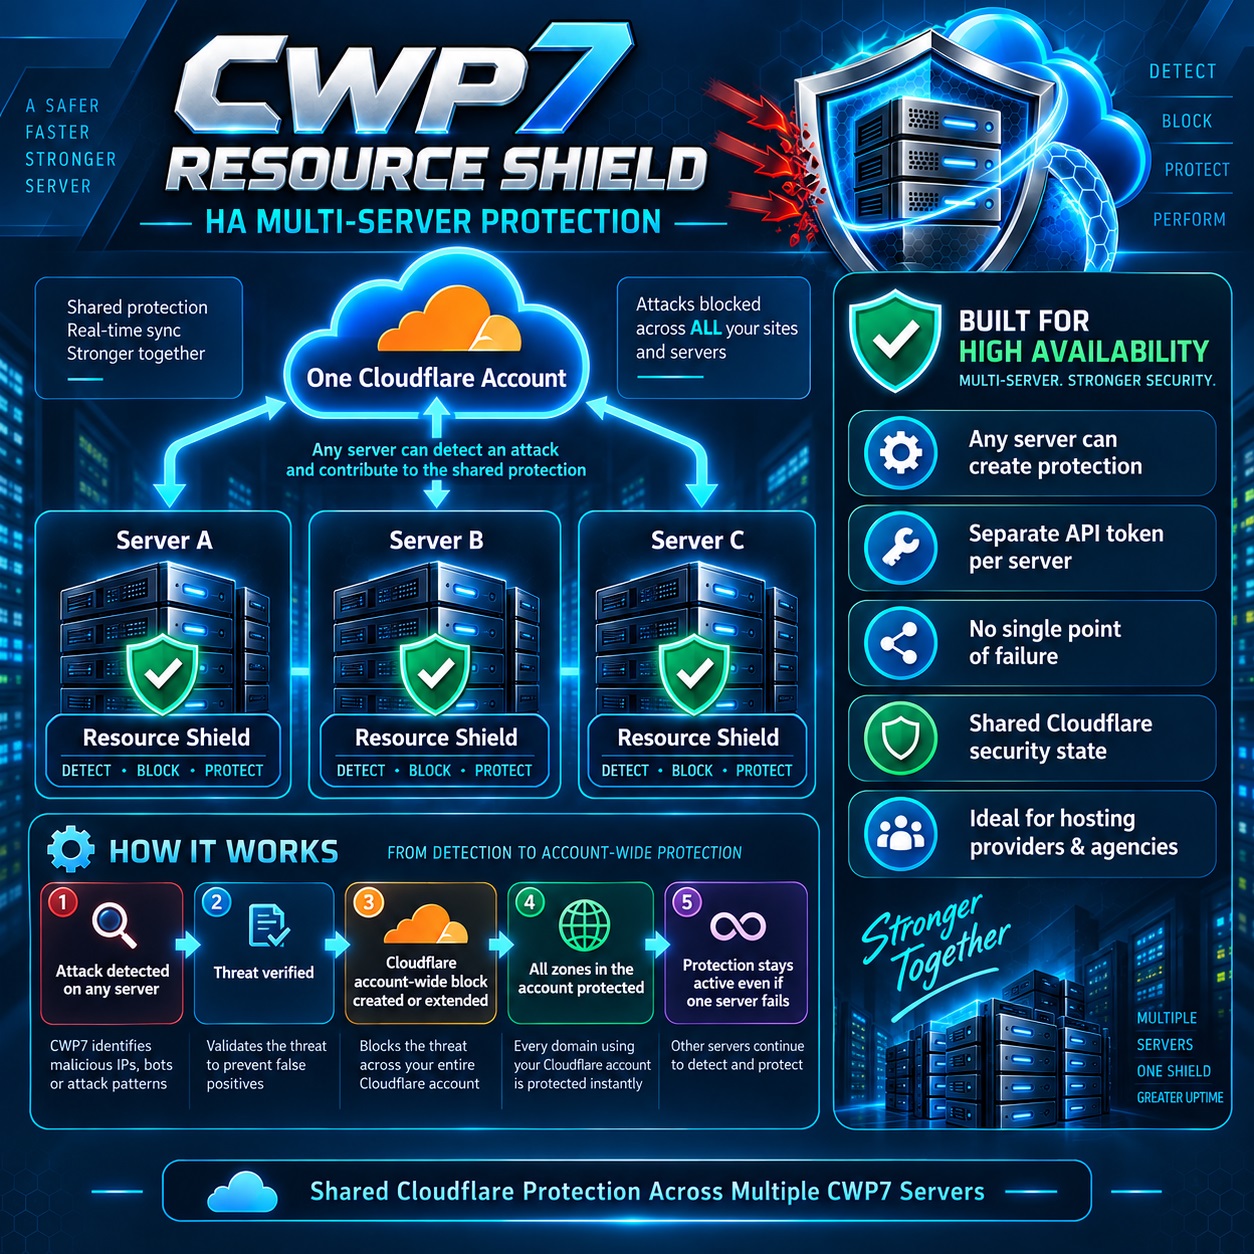
Multiple CWP7 servers can contribute attack intelligence to the same Cloudflare account-wide protection architecture.
A Central Security View Inside CWP7
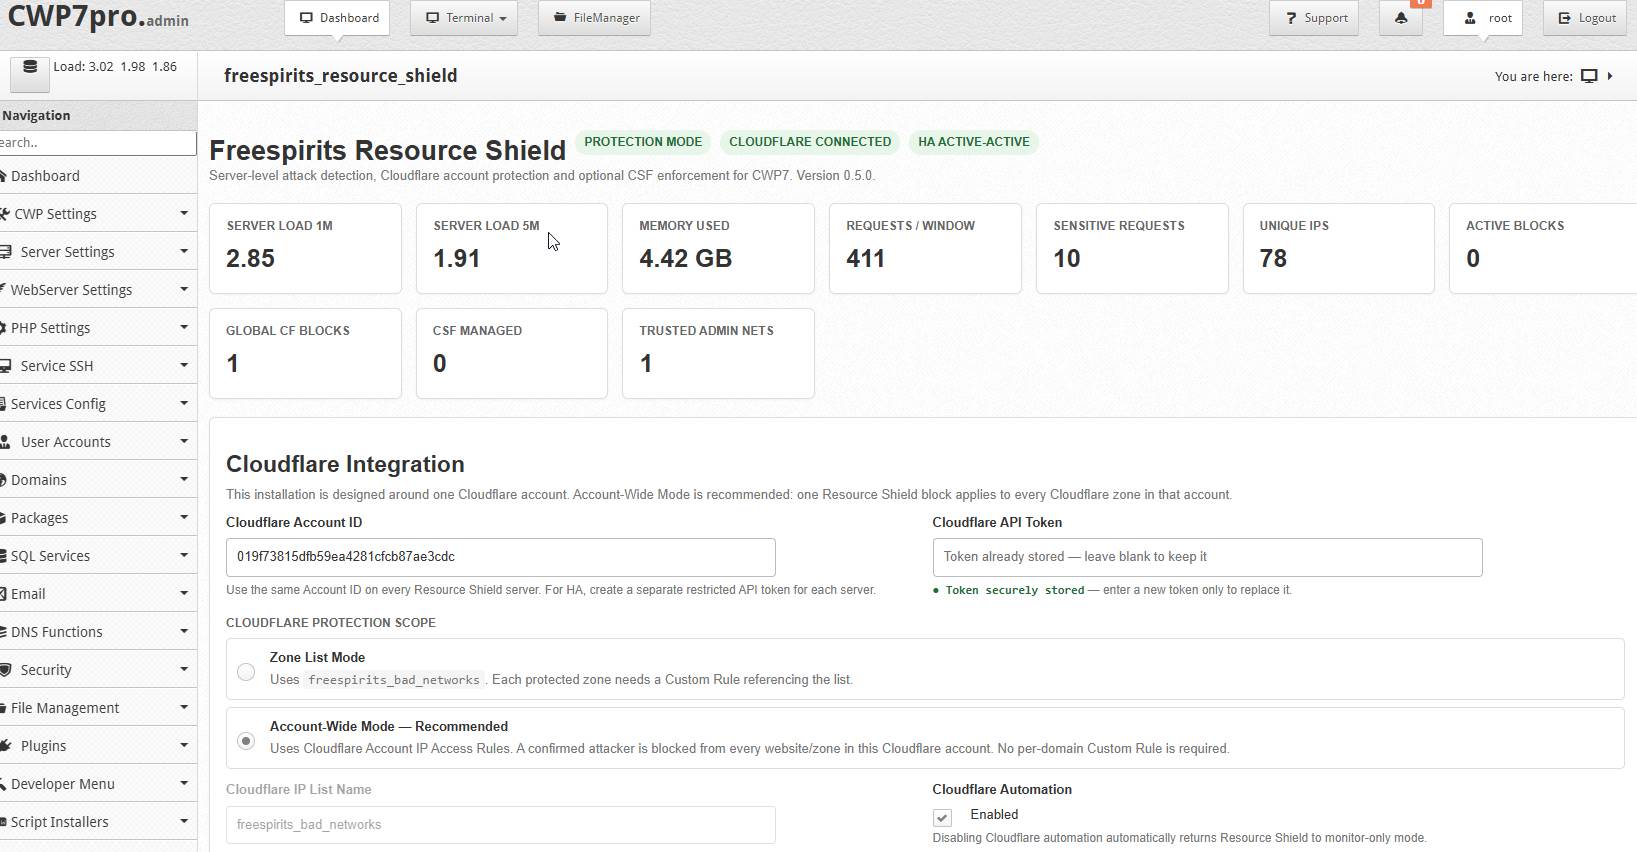
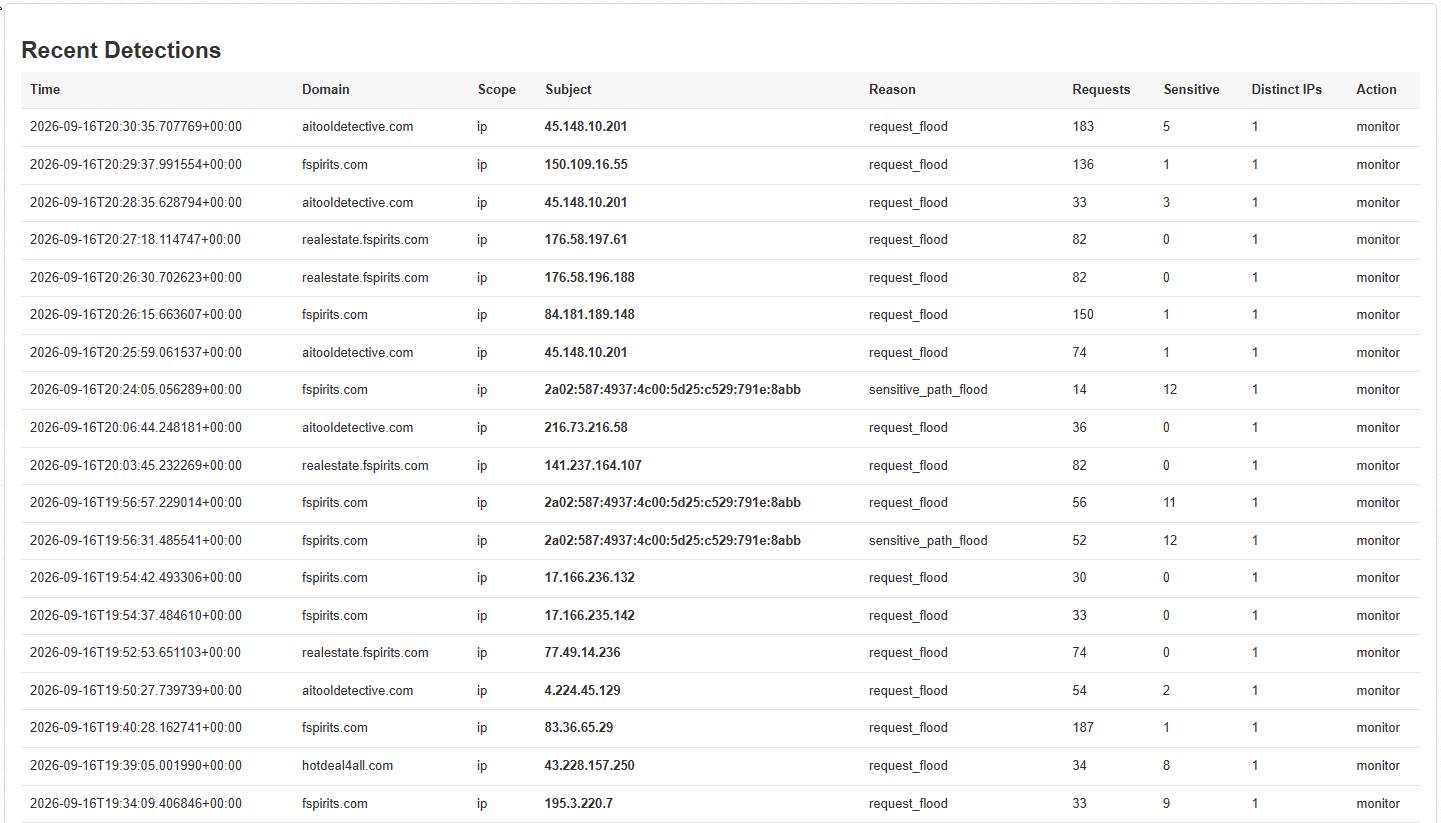
Resource Shield includes its own native CWP administration module, giving administrators fast access to important protection information from one central location.
- Resource Shield status
- Protection mode
- Διακομιστής load
- Requests being analysed
- Sensitive requests
- Unique requesting IPs
- Detected attacks
- Active blocks
- Cloudflare connectivity
- Account-wide protection
- Trusted administrator networks
- HA multi-διακομιστής protection
- Optional CSF integration
- License status
Instead of opening dozens of WordPress dashboards trying to understand why a διακομιστής is struggling, administrators gain a broader view of potentially abusive activity affecting the machine.
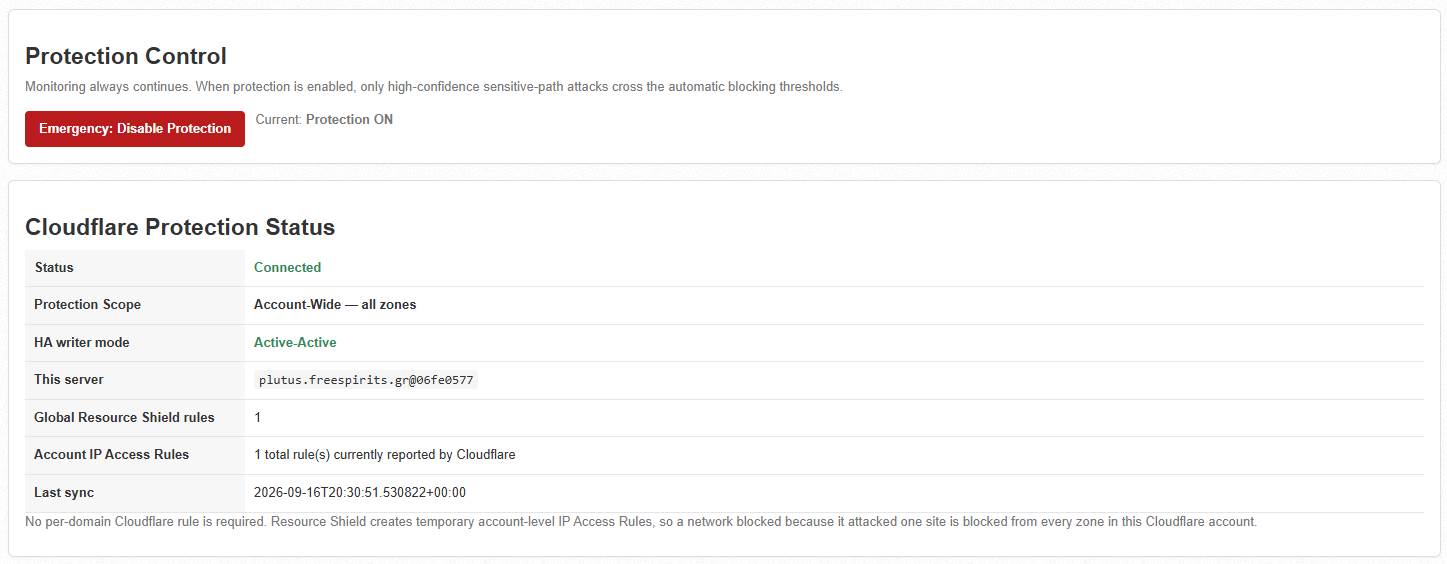
Cloudflare Account-Wide Protection
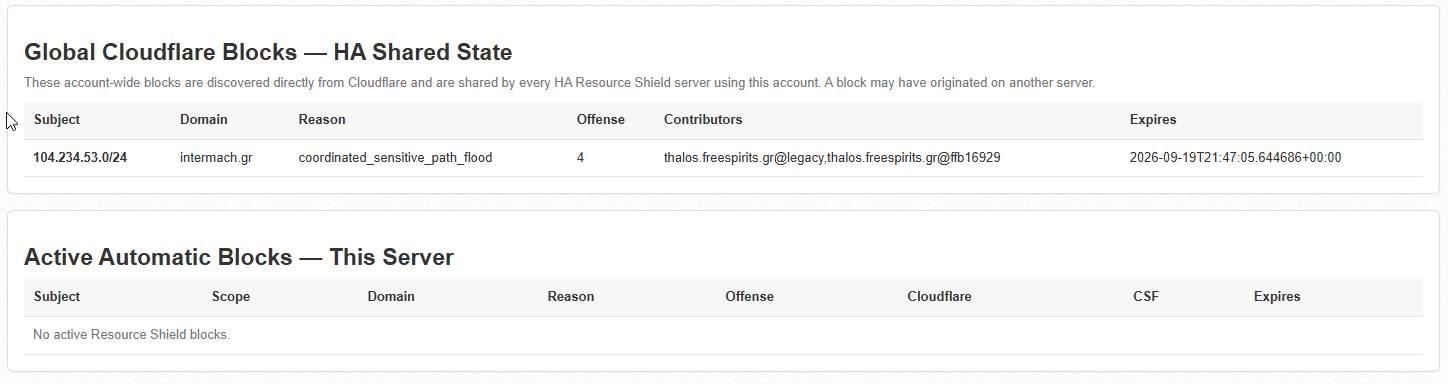
One of Resource Shield’s most powerful capabilities is the ability to turn an attack discovered against one website into protection that can benefit other websites connected to the same Cloudflare account.
Detected malicious network: 185.123.45.0/24
When Resource Shield creates the corresponding account-level Cloudflare protection, the attacking network can then be prevented from reaching additional protected websites.
An attack detected against one site can become useful security intelligence for the rest of your infrastructure.
High Availability Active-Active Multi-Διακομιστής Προστασία
Resource Shield is especially powerful for φιλοξενία providers, agencies, developers and administrators operating several CWP7 servers.
Every participating διακομιστής can independently detect threats and contribute to shared Cloudflare protection.
There is no requirement for one Resource Shield installation to function permanently as a master node.
If one διακομιστής becomes unavailable, Cloudflare blocks that have already been created continue to exist, while other Resource Shield servers can continue detecting new threats.
Stop Chasing Individual IP Addresses
Modern automated attacks frequently rotate through multiple IP addresses.
Blocking only:
may have limited effect when the next requests arrive from:
104.234.53.63
104.234.53.91
Resource Shield is designed to recognise coordinated behaviour and, when appropriate under its configured protection logic, escalate protection to the corresponding network:
This can significantly reduce the volume of repetitive attack requests allowed to continue reaching the origin διακομιστής.
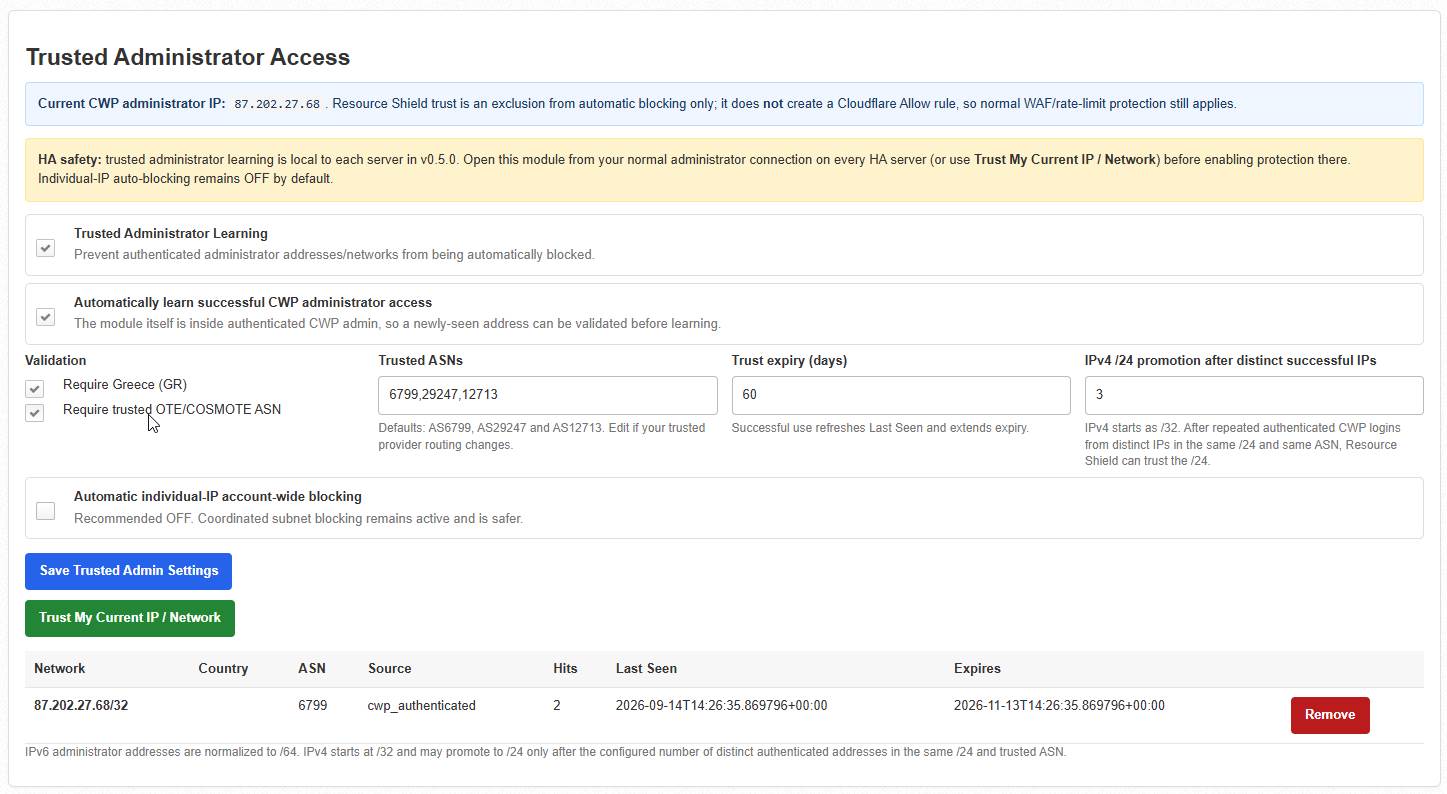
Trusted Administrator Protection
Automatic blocking is useful only when legitimate administrators are protected from accidental automated decisions.
Resource Shield therefore supports Trusted Administrator Access.
Trusted administrator connections can be excluded from the module’s automated attack-blocking logic.
IPv6 environments are also supported by allowing trusted administrator network handling rather than depending exclusively on one temporary IPv6 address.
Designed to Fight PHP-FPM Resource Exhaustion
High bandwidth is not always what brings down a WordPress φιλοξενία διακομιστής.
The expensive part is often what happens after a malicious request reaches PHP.
Repeated abusive requests may trigger:
- PHP-FPM workers
- WordPress execution
- WooCommerce database queries
- WP-Cron processes
- Action Scheduler jobs
- plugin execution
- additional RAM consumption
- additional CPU consumption
Eventually a PHP-FPM pool can reach its worker limits, while legitimate visitors begin waiting for available resources.
503 Service Unavailable
504 Gateway Timeout
Resource Shield is designed to reduce repeated malicious traffic reaching these expensive layers once threatening behaviour has been identified.
Resource Shield + Cgroups: Two Different Jobs, One Stronger Διακομιστής
CWP7 Resource Shield does not replace Cgroups.
Resource Shield concentrates on abusive traffic.
Cgroups help prevent an individual φιλοξενία account from consuming unlimited resources even when the traffic itself is legitimate or an application becomes unstable.
Used together, they provide a much more complete resource-protection strategy.
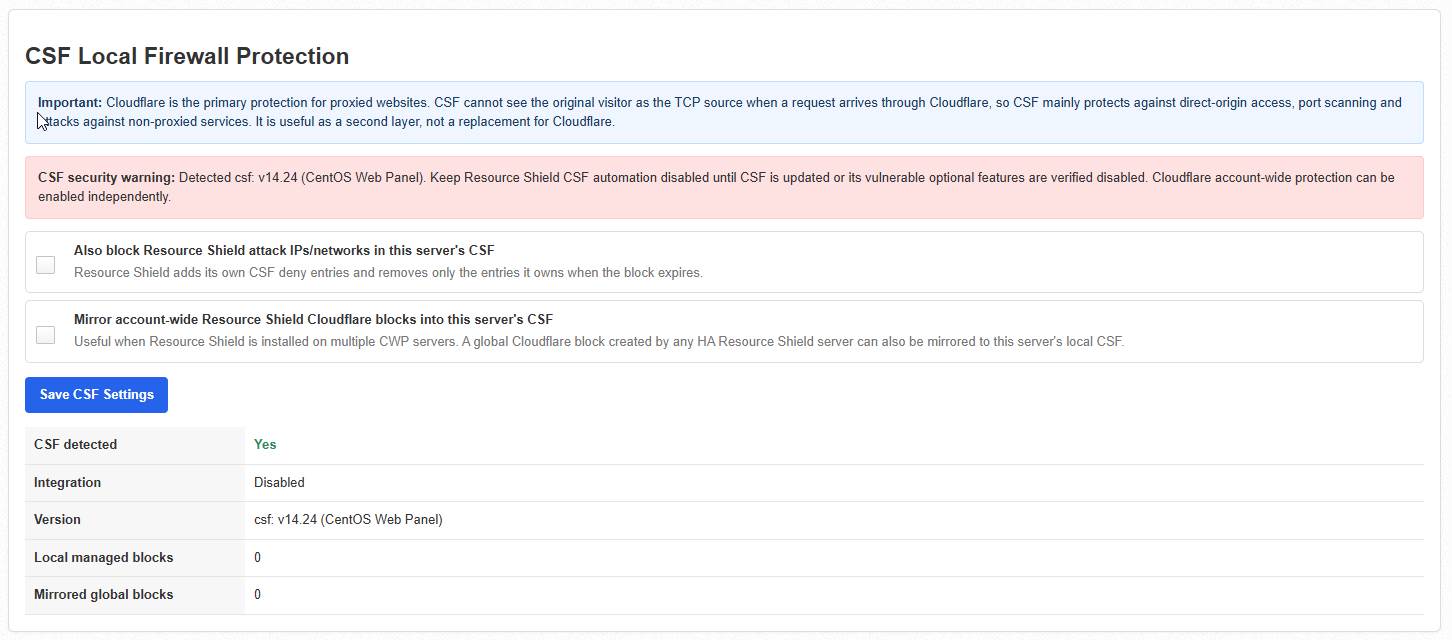
Optional CSF Integration
Cloudflare primarily protects traffic passing through the Cloudflare network.
Resource Shield can also work alongside compatible CSF installations for additional local firewall protection.
CSF may be useful for threats involving:
- direct origin traffic
- SSH attacks
- SMTP attacks
- port scanning
- non-proxied services
- websites not routed through the Cloudflare proxy
Cloudflare and CSF protect different parts of the infrastructure and can therefore complement each other.
Start Safely With Monitor Mode
Monitor Mode
Analyse activity and record detections without automatically creating new Cloudflare protection rules. Ideal for reviewing normal διακομιστής behaviour after installation.
Protection Mode
After configuration and validation, enable Protection Mode so confirmed threats can trigger the configured Cloudflare protection automatically.
A WordPress Plugin Sees a Website.
Resource Shield Sees the Διακομιστής.
Website security plugins remain valuable, but they operate primarily within their individual applications.
Resource Shield works from a different perspective. It is designed to observe activity affecting the φιλοξενία διακομιστής, correlate suspicious traffic and help prevent confirmed malicious sources from repeatedly consuming shared infrastructure.
That difference matters when dozens of websites depend on the same CPU, RAM, PHP-FPM pools and database διακομιστής.
A Practical Layered Defense for CWP7
Attack Detection + Automated Protection
Per-Account Resource Limits
Ποιος είναι CWP7 Resource Shield For?
- CWP7 φιλοξενία providers
- διακομιστής administrators
- web developers
- φιλοξενία resellers
- digital agencies
- managed WordPress providers
- WooCommerce φιλοξενία environments
- VPS administrators
- multi-διακομιστής infrastructures
- Cloudflare users
- servers experiencing PHP-FPM saturation
- administrators wanting centralised attack visibility
If You Have Ever Seen This…
- A customer’s WordPress site gets attacked and the whole VPS slows down.
- PHP-FPM suddenly reaches its worker limits.
- CPU usage jumps without a legitimate traffic increase.
- Hundreds of requests hit
wp-login.phpήxmlrpc.php. - WooCommerce becomes slow because another hosted account is under attack.
- You manually block one IP only to see the attack continue from another.
- You manage dozens of websites and cannot investigate every WordPress installation individually.
That is exactly the type of φιλοξενία environment Resource Shield was created to address.
Simple Διακομιστής Licensing
1 Resource Shield License = 1 Activated CWP7 Διακομιστής
Licensing is handled through the Freespirits licensing system.
During activation, the license becomes associated with the διακομιστής installation and cannot simply be copied to an unrelated VPS.
For legitimate διακομιστής migrations, the activation can be reviewed and reset according to the applicable licensing terms.
Cloudflare Requirements
For automated Cloudflare protection you will need:
- A Cloudflare account
- Protected domains configured in Cloudflare
- A dedicated Cloudflare API Token
- The required account firewall permissions
Create a dedicated Cloudflare API token specifically for Resource Shield. Do not use your Cloudflare Global API Key.
For multi-διακομιστής deployments, use a separate restricted token for each διακομιστής whenever possible.
Cloudflare Setup
Create a dedicated API token from:
Provide the required Account Firewall Access Rules: Edit permission for the Cloudflare account you want Resource Shield to protect.
For additional security, restrict the token under Client IP Address Filtering to the public IP address of the corresponding CWP7 διακομιστής whenever appropriate.
Your Cloudflare Account ID can be copied from the Cloudflare Dashboard and entered into the Resource Shield configuration.
Straightforward Installation
After obtaining the Resource Shield package, upload it to your CWP7 διακομιστής and connect through SSH as root.
cd /root
unzip freespirits-resource-shield-*.zip
cd freespirits-resource-shield-*/
chmod +x install.sh
./install.sh
After installation, verify the service:
Then check Resource Shield itself:
Open the CWP7 administrator interface and navigate to:
Activate your license and configure your Cloudflare Account ID and dedicated API token.
Useful Administration Commands
Overall status
License status
Validate license
View active blocks
Trusted administrator networks
HA information
Recent activity
Part of a Layered Security Strategy
Resource Shield is an additional security and resource-protection layer. It is not intended to replace:
- strong passwords and secure administrator access
- WordPress and plugin updates
- operating-system updates
- regular backups
- malware scanning
- Cloudflare configuration
- CSF
- Cgroups
- PHP-FPM tuning
- professional διακομιστής administration
Instead, Resource Shield complements these systems by focusing on a specific and extremely important problem:
Protect the Διακομιστής, Not Just One Website
If you operate a CWP7 διακομιστής, every hosted customer ultimately depends on the health of the same underlying infrastructure.
A single attacked website should not be allowed to consume enough PHP, CPU, RAM or database capacity to affect every other customer.
CWP7 Resource Shield adds the διακομιστής-level visibility and automated protection needed to identify coordinated abusive traffic and push confirmed threats outward toward Cloudflare.
CWP7 Resource Shield
Διακομιστής-Level Attack Detection & Cloudflare Protection for Control Web Panel
Developed by Υπηρεσίες Ιστού Freespirits